
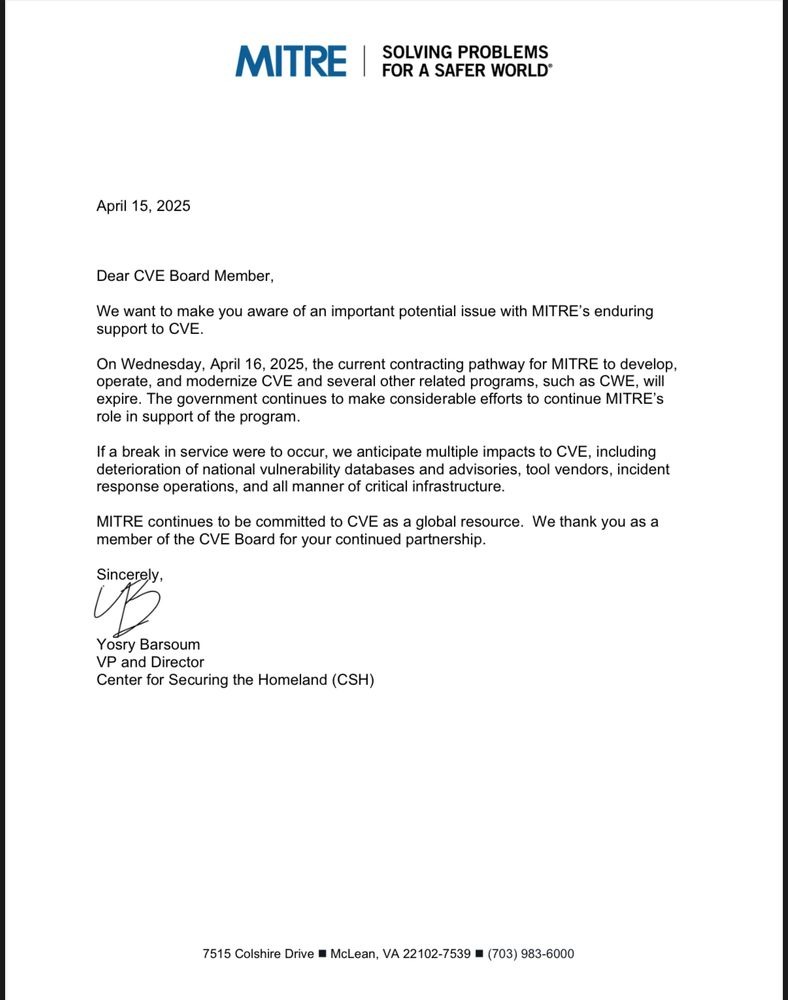


MITRE, a vital organization responsible for managing the Common Vulnerabilities and Exposures (CVE) program, issued a warning regarding the potential breakdown of this critical cybersecurity resource. The contract to maintain the CVE program, which is traditionally funded annually by the Department of Homeland Security, is set to expire on April 16th, putting the future of this essential service in jeopardy.
Every year, tens of thousands of security vulnerabilities in software are identified and reported, leading to the assignment of unique CVE tracking numbers to each issue. These CVE numbers are crucial for organizations to track and address vulnerabilities effectively. MITRE authorizes various organizations, known as CVE Numbering Authorities (CNAs), to assign CVE numbers to newly reported flaws, ensuring a standardized approach to addressing software vulnerabilities.
The CVE program serves as a central repository for information on software vulnerabilities, enabling organizations to identify and patch security holes promptly. Without this centralized resource, the cybersecurity community would lose a key tool for managing and discussing vulnerabilities consistently.
Yosry Barsoum, Vice President at MITRE, sent a letter to the CVE board warning about the impending expiration of the organization’s contract to operate and update the CVE program. If this contract is not renewed, multiple impacts are expected, including the deterioration of national vulnerability databases, tools, and incident response operations that rely on CVE information.
While MITRE confirmed that the CVE website will remain accessible after the funding expires, new CVEs will not be added post-April 16th. The potential disruption of the CVE program raises concerns about the ability of organizations to stay informed about emerging vulnerabilities and adequately protect their systems.
Former CISA Director Jen Easterly likened the CVE program to the Dewey Decimal System, emphasizing its role as a global catalog for organizing and discussing cybersecurity vulnerabilities. Without the CVE program, there is a risk of confusion and inefficiency in addressing security issues, ultimately benefiting threat actors seeking to exploit vulnerabilities.
Security experts, including John Hammond from Huntress, expressed dismay over the imminent funding crisis facing the CVE program. Losing access to CVE numbers could impede the ability of cybersecurity professionals to communicate effectively and prioritize security measures.
Despite the uncertainty surrounding the CVE program’s funding, efforts are underway to secure continued support for MITRE’s role in maintaining the program. The potential consequences of a lapse in funding for the CVE program underscore the importance of sustaining this critical cybersecurity resource for the protection of digital infrastructure worldwide.
In conclusion, the cybersecurity community is closely monitoring the situation, hoping for a resolution to ensure the uninterrupted operation of the CVE program. The collaborative efforts of government agencies, private organizations, and cybersecurity professionals are essential to safeguarding digital systems against evolving threats and vulnerabilities.