
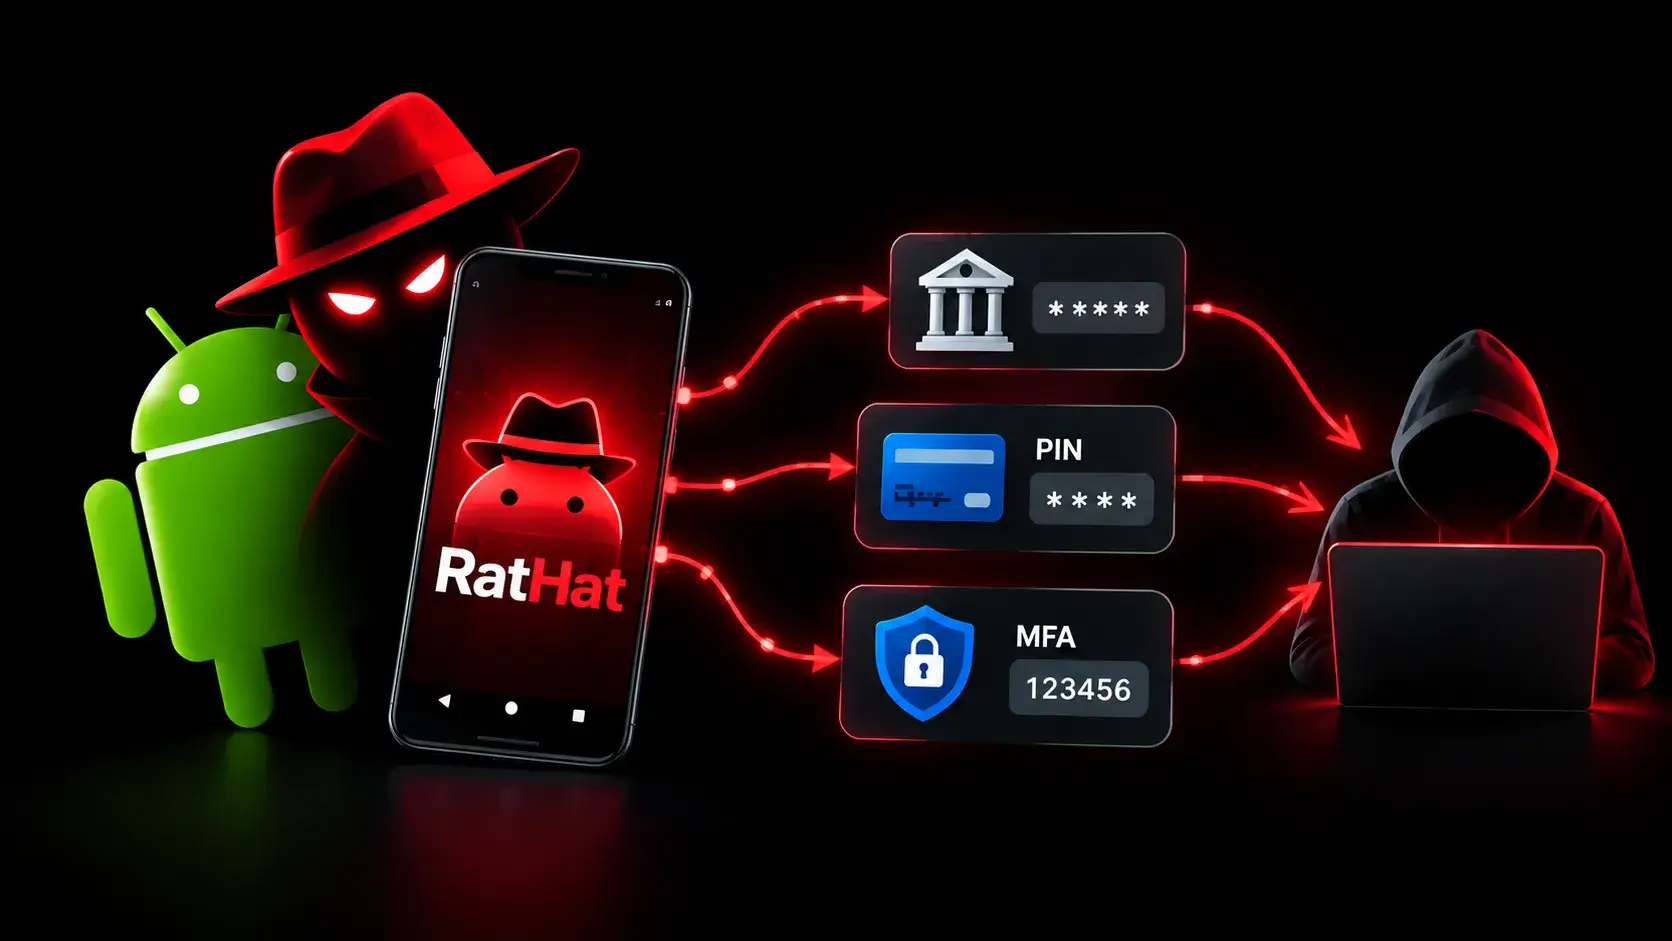
A New Threat Emerges: The AI-Powered RatHat Android Trojan
In a significant advancement in the realm of cybersecurity, researchers have uncovered a newly identified Android banking Trojan known as RatHat. This innovative malware leverages artificial intelligence to automate the compromise of devices, facilitating the theft of sensitive financial credentials, such as PINs and one-time passcodes. The analysis conducted by Zimperium’s zLabs researchers indicates that RatHat marks a notable evolution in the threats facing Android users.
Sophisticated Mechanisms of Attack
The mechanisms employed by RatHat are distinctly different from traditional malware. Instead of relying on fixed scripts, this Trojan operates with a live AI service that has the capability to access the Android accessibility tree. This advanced functionality allows the AI to examine various on-screen elements, thereby making autonomous decisions about where to tap, scroll, or input information during the attack. Consequently, RatHat poses a significant challenge for conventional mobile security solutions which may struggle to detect such nuanced operations.
The infection process for RatHat is initiated through social engineering tactics, such as smishing messages and malicious advertisements. These deceptive strategies aim to redirect users to counterfeit download pages masquerading as popular applications, including well-known streaming services or widely used web browsers. Vulnerable individuals are often persuaded to download a malicious APK from sources outside of the Google Play Store and other reputable app marketplaces.
Once installed, RatHat employs psychological manipulation to pressure users into enabling the Android Accessibility Service. The malware may present false alerts regarding network restrictions or assert that enabling this permission is a prerequisite for receiving financial advantages. This particular strategy is particularly hazardous, as accessibility permissions grant apps the ability to inspect screen content and perform actions on the user’s behalf, creating an opportunity for malicious exploitation.
The Intricacies of Accessibility and Remote Connection
After gaining the necessary accessibility permissions, RatHat can deftly navigate through various Android settings to enable Wireless Debugging. By reading the six-digit pairing code displayed on the device, it can establish an Android Debug Bridge (ADB) connection. ADB is typically a legitimate tool utilized by developers for testing and managing their Android devices, but in this case, RatHat has repurposed it to extend its capabilities beyond those permitted for ordinary applications.
The malware’s sophistication comes into play as it establishes two disguised native components post-ADB session initiation. One component is a Go-based agent tasked with executing commands on the compromised device, while the other serves as a reverse proxy, sustaining a persistent connection to infrastructure controlled by the attackers. This connection facilitates remote access to the device while circumventing common network restrictions such as firewalls and NAT environments.
According to MalwareBytes, RatHat specifically targets financial applications with credential-harvesting overlays that mimic legitimate banking interfaces. These overlays are designed to capture critical user information, including usernames, passwords, card details, and one-time passwords used in multi-factor authentication systems. Additionally, the Trojan has the capability to intercept SMS messages, thereby putting transaction verification codes directly in the reach of malicious actors.
Disturbing Features and Preventative Measures
One of the most worrisome characteristics of RatHat is its ability to gather raw touch coordinates from the device’s input driver. This feature enables the malware to compare these coordinates against known keypad and pattern-lock layouts, effectively reconstructing PINs and unlock patterns. By employing this technique, RatHat can bypass established protections designed to prevent malware from reading sensitive information directly from the screen.
Moreover, RatHat features persistence capabilities that may allow it to reinstall or restore its components even after users believe they have removed the visible malicious application. For individuals suspected of being infected, a factory reset of the device is recommended to eliminate any lingering threats.
In light of this evolving threat, users are urged to exercise caution by only installing applications from trusted sources and denying unnecessary accessibility requests. It is also advisable to refrain from enabling Developer Options or Wireless Debugging unless users fully comprehend the implications of these settings.
As cybersecurity threats continue to evolve, it remains crucial for users to stay informed and vigilant against such sophisticated malware. The emergence of A.I.-powered threats like RatHat demonstrates the ongoing arms race between cybersecurity measures and malicious actors, underlining the need for enhanced protective strategies in the digital landscape.