
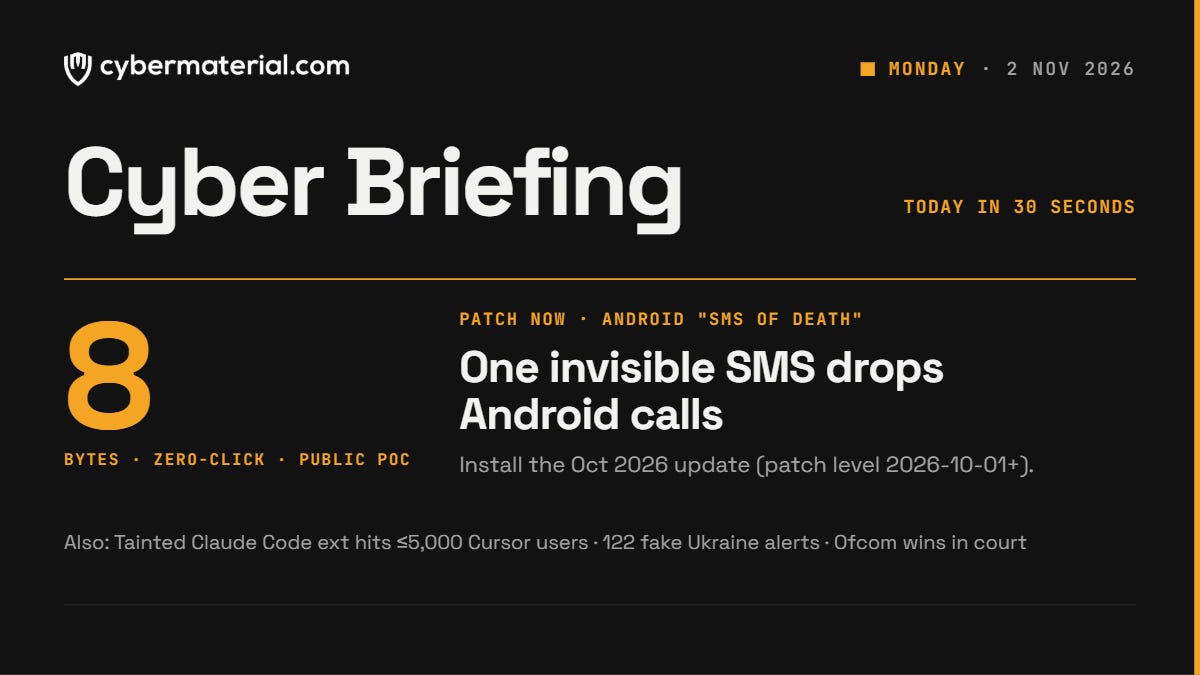


Cybersecurity Updates: Recent Threats and Legal Developments
In an ever-evolving landscape of cybersecurity threats, recent developments reveal significant vulnerabilities and implications across various platforms and nations. A major highlight involves a critical zero-click vulnerability found in Android systems. This flaw in the WAP Push SMS handling allows malicious actors to crash phone services simply by sending a specifically crafted SMS message. Affected devices range from Android 12 to 17, with the flaw having been designated as CVE-2026-58882. This vulnerability disrupts active calls, including emergency services, presenting potential danger to users who may depend on their devices during critical situations.
To counteract this risk, Google has released patches in its October 2026 security update for devices running Android 14 to 17. However, users of Android 12 and 13 face lingering vulnerabilities, depending on their respective manufacturers to implement timely updates. This situation brings to the forefront the importance of being vigilant about software updates, as the consequences of negligence could prove fatal in emergency situations.
In a separate incident, cybersecurity experts have uncovered a serious breach involving extensions masquerading as Claude AI within the Cursor code editor. Distributed through a supply chain attack, this malicious extension aimed to establish a reverse SSH tunnel, granting hackers unauthorized remote access to affected systems. Alarmingly, it is estimated that this extension impacted around 5,000 machines, urging developers to audit their installed extensions and remove any unauthorized packages associated with Claude AI. This breach underscores the need for comprehensive security practices, highlighting how supply chain vulnerabilities can be exploited to infiltrate otherwise secure environments.
Adding to the list of cybersecurity challenges, a coordinated attack targeting emergency alert applications in Ukraine and Russia took place recently, with hackers disseminating false alerts about nuclear threats and chemical attacks. These deceptive messages were broadcasted to millions of users, creating panic and confusion amidst ongoing conflict. In response, both governments temporarily disabled their alert apps, advising citizens to rely on alternative warning systems and official communications until the situation is contained. Such incidents illustrate the intricate interplay between cyber warfare and public safety, as misinformation can have devastating real-world consequences.
In the context of regulatory measures, the UK High Court has ruled in favor of Ofcom, the UK’s communications regulator, against social media giants Meta, TikTok, and X, regarding compliance with the Online Safety Act. The court upheld Ofcom’s authority to demand data about content moderation practices, user activity segmented by age group, and exposure to harmful content among UK users. This landmark decision marks the first judicial review under the new legislation, reinforcing the regulator’s data gathering powers and potentially setting a precedent for further actions against non-compliance.
Amidst these challenges, a prominent firm has taken proactive measures in the realm of artificial intelligence. Cognizant has launched an initiative named the OpenAI Frontier Capability Group, composed of 25,000 employees aimed at helping enterprises integrate OpenAI technologies such as ChatGPT and Codex into various aspects of their operations, including software development and customer service. Since the program’s inception, over 21,000 employees have earned more than 40,000 OpenAI badges through internal training, emphasizing the growing importance of AI in enhancing businesses’ technological capabilities. This initiative also highlights a wider industry trend toward leveraging artificial intelligence for operational efficiency and innovation.
As threats burgeon and as technology evolves, entities across sectors must remain vigilant to safeguard their systems and users. Regular software updates, thorough audits of third-party extensions, and compliance with regulatory standards are essential in mitigating risks. In an era where the digital landscape is increasingly interwoven with real-world implications, proactive cybersecurity measures and legal clarity serve as vital cornerstones for safety and accountability.