
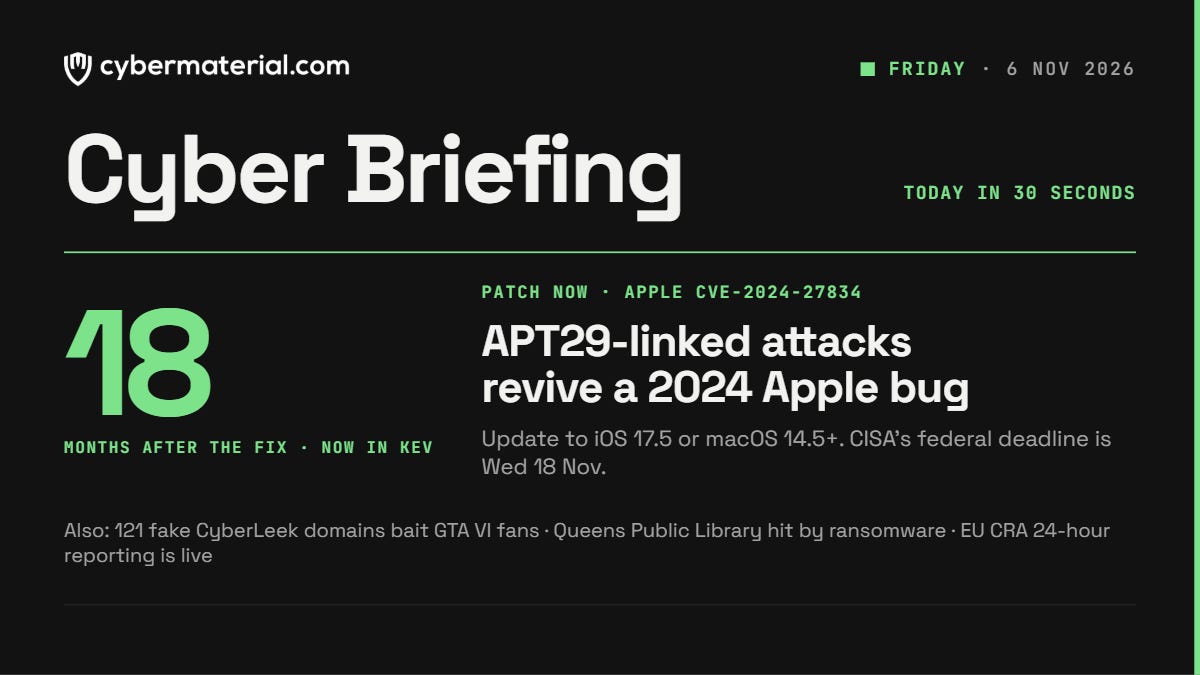


Cybersecurity Briefing: Notable Updates on Vulnerabilities and Scams
In the ever-evolving landscape of cybersecurity, recent reports from the Cybersecurity Infrastructure and Security Agency (CISA) underscore critical vulnerabilities and pressing threats that organizations and individuals worldwide must heed. This briefing highlights significant updates regarding vulnerabilities, fraud in the gaming industry, and incidents affecting public institutions.
Apple Vulnerability CVE-2024-27834
The CISA recently added a new vulnerability, CVE-2024-27834, to its Known Exploited Vulnerabilities (KEV) catalog, following reports of attacks linked to the advanced persistent threat group APT29, which is believed to have ties to Russian state-sponsored activities. This security flaw allows malicious actors who already have memory access to bypass the Pointer Authentication Code (PAC) security protections inherent in Apple silicon processors. As a result, their ability to carry out memory corruption exploits is significantly heightened.
Federal agencies have been mandated to patch all affected Apple devices by November 18, 2026. However, private organizations are also urged to prioritize updates across various operating systems, including Safari, iOS, iPadOS, macOS, tvOS, and watchOS. Given the potential ramifications of this vulnerability, timely updates are paramount for system security.
Exploitation of Gaming Anticipation
In a concerning trend, cybercriminals are seizing on the hype surrounding the upcoming release of Grand Theft Auto VI, slated for launch on November 19. Research conducted by Netcraft has revealed a staggering 121 fraudulent domains linked to the game, designed to entice eager gamers with promises of leaked builds, early access, and even mobile versions of the anticipated title. Among these impersonations is a site masquerading as the well-known game leak platform, CyberLeek.
The scams have resulted in the dissemination of malware and cryptocurrency frauds, posing a substantial risk to users seeking unauthorized versions of the game. The proliferation of these deceptive sites highlights the importance of vigilance and skepticism, especially during high-profile game releases.
Ransomware Attack on Queens Public Library
In a significant blow to public services, the Queens Public Library in New York City confirmed that it has fallen victim to a ransomware attack. The attack has effectively disabled various operational aspects, including the library’s website, computer systems, checkout operations, Wi-Fi, and mobile application, although its physical branches remain accessible to patrons.
At this juncture, no ransomware group has publicly claimed responsibility for the attack. Experts emphasize that attacks on public institutions often yield lower payouts for cybercriminals, but this does not diminish the challenging and costly recovery process that lies ahead. The library’s IT team has commenced recovery efforts, but the timeline for full restoration remains uncertain. For perspective, a similar situation faced by the British Library in 2023 resulted in projected recovery timelines extending until 2026.
Upcoming EU Cyber Resilience Act
On the legislative front, the European Union’s Cyber Resilience Act (CRA) has introduced new requirements for network-connected products sold within its member states. By December 11, 2027, manufacturers will need to ensure all such products meet specific cybersecurity standards. Since September 2024, there has also been a requirement for manufacturers to report any actively exploited vulnerabilities within a mere 24 hours, with severe penalties for non-compliance, potentially reaching €15 million or 2.5% of global revenue.
Security experts caution that the deadline is rapidly approaching, urging manufacturers to begin their compliance efforts immediately. The implications of these new rules extend beyond Europe, as global product standards may eventually align with stricter EU regulations.
AI Agent Detection Challenges
In a related context, advancements in AI technology have spurred the emergence of AI agents capable of performing tasks in ways distinct from traditional bots. These agents can operate with declared, undeclared, or disguised traffic, complicating detection efforts for cybersecurity teams. Resemble AI’s CEO, Zohaib Ahmed, notes that classical binary detection systems may fail to identify undeclared and disguised traffic effectively. Consequently, organizations should refine their detection techniques, incorporating parameters like click timing patterns and multiple sessions targeting the same goal to improve outcomes.
As the cybersecurity landscape continues to evolve, staying informed and proactive remains essential. Whether dealing with newly identified vulnerabilities, navigating the threats of cyber scams, or understanding the legislative changes on the horizon, organizations must prioritize robust security measures to safeguard their digital environments. The highlighted incidents and developments serve as a stark reminder of the persistent threats that inhabit our increasingly digitized lives.