


Cybersecurity Brief: Apple Patches Vulnerabilities and Vanderbilt University Faces Ransomware Attack
In a series of crucial cybersecurity developments, Apple has rolled out security updates addressing nine vulnerabilities across its operating systems while Vanderbilt University deals with the ramifications of a ransomware attack that has disrupted its services. This assemblage of events highlights the ongoing challenges and risks in the digital landscape.
Urgent Patches for Apple Devices
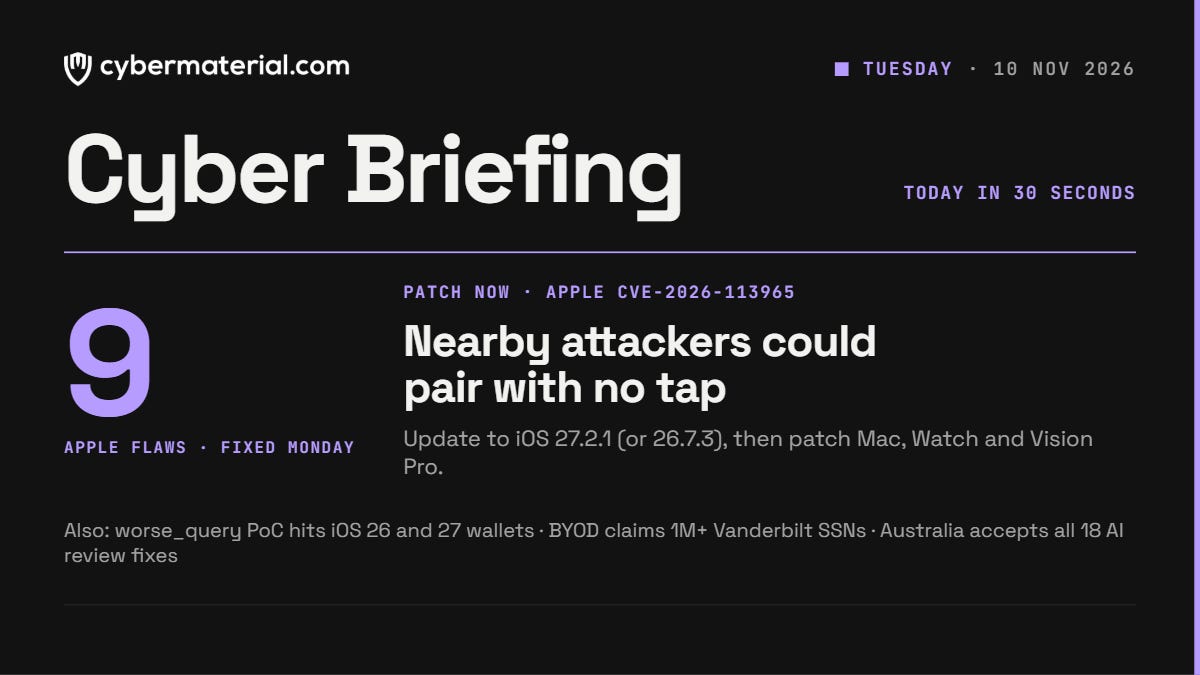
On Monday, Apple announced the release of security updates for iOS, iPadOS, macOS, watchOS, and visionOS aimed at plugging nine critical vulnerabilities, particularly those linked to Bluetooth connectivity. Notably, one of the flaws, identified as CVE-2026-113965, could allow nearby Bluetooth devices to initiate a pairing process without needing user interaction. This vulnerability poses a significant risk, as it could enable unauthorized access and manipulation of devices if not addressed promptly.
Apple’s users are strongly advised to install these updates immediately to mitigate potential threats that could arise from unapproved device connections. Many observers recognize the increase in Bluetooth-related vulnerabilities as a pressing concern, especially in an age where seamless connectivity is often prioritized over security.
In addition to the Bluetooth shortcomings, a significant security threat has been identified in the form of a publicly disclosed sandbox escape vulnerability dubbed “worse_query.” This issue exists in iOS 26 and 27, and it allows malicious applications to read files from other applications installed on the same device. This exploit could compromise sensitive information such as cryptocurrency wallet seed phrases and private keys, raising alarms among tech consumers, particularly those with substantial digital assets. Notably, Binance, a prominent cryptocurrency exchange, has issued warnings urging users to secure their devices to avoid potential theft of funds.
Ransomware Attack at Vanderbilt University
Simultaneously, Vanderbilt University is grappling with a severe ransomware attack claimed by the BYOD ransomware group. Since Monday, the attack has disrupted access to several university systems. The attackers assert that they have stolen over one million Social Security numbers along with student and employee records, although the university has not yet confirmed these claims. Despite the chaos, university classes have continued as scheduled; however, the IT department is working diligently with governmental agencies to restore systems while investigating the breach’s extent.
The BYOD group is notorious for its aggressive tactics, and the nature of their accusation underscores a growing trend that highlights the vulnerabilities educational institutions face. Many universities are seen as prime targets due to their extensive databases of personal and sensitive information and the relatively lower levels of cybersecurity measures compared to the private sector.
Australia’s New Regulations for AI Companies
Turning to developments in Australia, the government has announced plans to introduce mandatory breach reporting requirements for artificial intelligence companies. This follows a major data breach involving OpenAI associated with the country’s Medicare system. Despite the serious nature of this incident, OpenAI has not faced criminal penalties. Prime Minister Anthony Albanese highlighted that this issue emphasizes the necessity for clear accountability among AI firms, especially those handling sensitive governmental or citizen data.
The new legislation designed to mandate breach reporting is a proactive step toward ensuring that organizations are held accountable for their cybersecurity practices. This initiative is particularly relevant in today’s fast-evolving digital environment where the intersection of technological advancement and data security remains a delicate balance.
Broadcom’s Contribution to the Cloud Native Computing Foundation
In a move aimed at addressing concerns over vendor lock-in, Broadcom has contributed its Virtual Machine Application Programming Interface (VM API) to the Cloud Native Computing Foundation (CNCF). This API enables the unified management of virtual machines and containers on Kubernetes, providing a single interface with pluggable hypervisor support. The decision follows broad dissatisfaction with Broadcom’s recent pricing changes for VMware. By engaging in open-source strategies, Broadcom appears to be working hard to retain its customer base while modernizing infrastructure management procedures.
The combination of these significant events—Apple’s need for extensive patching, Vanderbilt’s handling of a ransomware crisis, Australia’s regulatory measures for AI firms, and Broadcom’s strategic donations to CNCF—underscores the ongoing risk landscape in cybersecurity. As technology evolves, so do the threats, making vigilance and proactive measures vital for individuals and organizations alike.