
Cybersecurity Brief: Latest Incidents and Advisories
In an age where cybersecurity threats are becoming increasingly sophisticated, today’s updates from Cyber Briefing encapsulate critical developments that demand immediate attention from organizations and individuals alike. As cyberattacks continue to evolve, being informed is essential for mitigating risks and responding effectively to incidents.
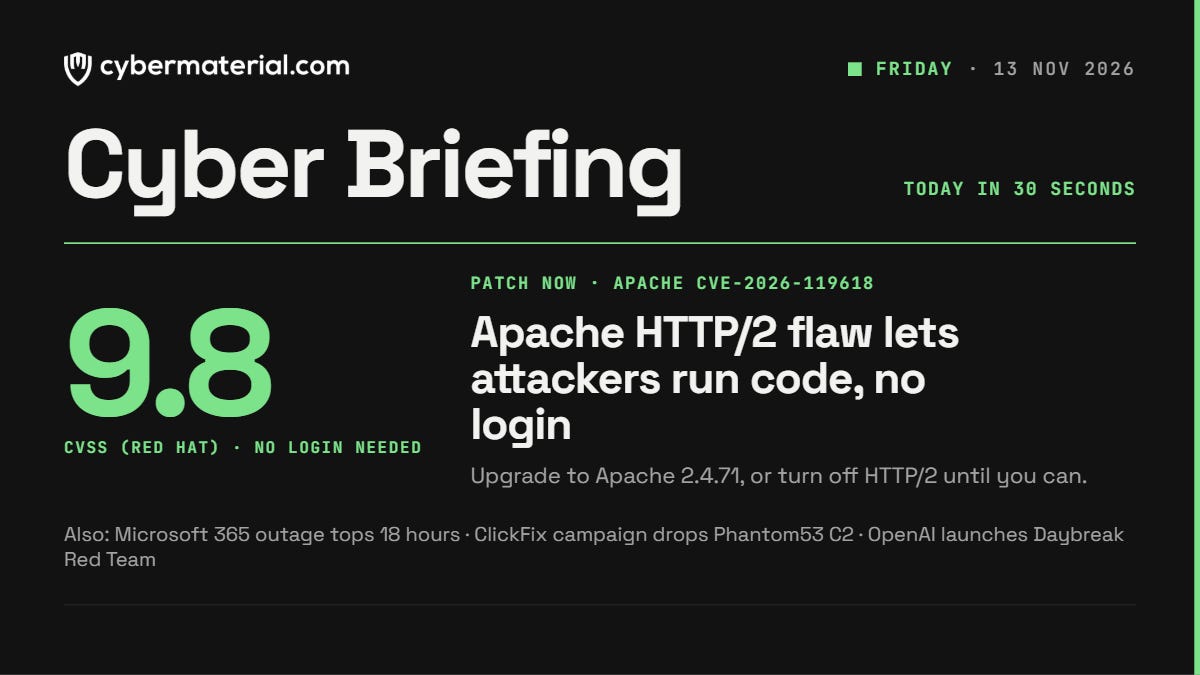
One of the most pressing issues highlighted today is the urgency for Apache users to patch their systems. The Apache Software Foundation announced the release of Apache HTTP Server version 2.4.71 on November 11, 2026, addressing a severe vulnerability tagged CVE-2026-119618. This flaw presents a significant risk due to a race condition in the HTTP/2 module (mod_http2). It’s crucial to note that versions 2.4.55 through 2.4.70 are susceptible to exploitation, particularly for systems with HTTP/2 enabled. Users who are unable to upgrade their Apache installations immediately should consider disabling HTTP/2 to prevent potential attacks.
Simultaneously, Microsoft’s 365 services faced an extensive outage that lasted over 18 hours, affecting numerous services, including Exchange Online, Teams, and cloud PC functionalities. The incident began on Thursday at 18:00 UTC and disrupted approximately 15 other hosted services as well. Despite Microsoft’s assurances that there was no indication of malicious activity behind the outage, the company struggled to restore services due to complications that arose, such as virtual machines becoming stuck in a broken state. While recovery was reported in North America and Europe by Friday afternoon, users in the Asia-Pacific region continued to deal with intermittent access difficulties.
An intriguing development in the cybersecurity landscape is the emergence of a ClickFix campaign, which has been noted for disseminating the Phantom53 malware. This malware cleverly conceals its command traffic within DNS-over-HTTPS, rendering it less detectable to standard security measures. Researchers reported that nearly 1,000 phishing pages targeting regions across Latin America, Asia, and Europe are promoting this threat. The actor behind this campaign remains unidentified, but it serves as a stark reminder of the persistent and intricate threats that online users face daily.
On the regulatory front, Binance has taken a proactive stance by proposing a "Know Your Agent" (KYA) framework in the financial sector. This initiative would mandate that every action performed by AI agents in financial transactions be tied back to an accountable human, thereby enhancing oversight and accountability. As AI continues to integrate into various aspects of financial services, establishing clear lines of responsibility becomes crucial in addressing concerns of regulatory compliance and ethical decision-making.
In a nod to preventative measures, OpenAI has unveiled two new security tools. The first, named Daybreak Red Team, deploys AI agents to conduct penetration testing on web applications, enhancing security assessment capabilities. The second tool, Defense Factory, aims to streamline the discovery of security vulnerabilities and facilitate the patching process. Organizations that utilize web applications should consider evaluating these AI-driven tools, which promise to automate significant portions of security testing and remediation workflows.
Meanwhile, organizations that deploy AI agents must remain vigilant against the risks associated with prompt injection attacks. These vulnerabilities arise when AI agents, equipped with access to sensitive systems, are manipulated via malicious instructions embedded in user inputs. This manipulation can lead to unauthorized actions, such as exporting crucial records to adversary-controlled destinations. The key to mitigating these risks lies in implementing stringent access controls, input validation, and monitoring to prevent agents from falling prey to instructions that exploit their permissions.
As the day unfolds, cybersecurity professionals and organizations are called to remain informed and proactive. Monitoring advisories, responding to vulnerabilities, and implementing preventive measures can substantially reduce the risk of becoming future targets of cybercriminals. By staying ahead of potential threats, maintaining vigilance, and investing in targeted safeguards, individuals and organizations can fortify their defenses and continue to thrive in an increasingly complex digital landscape.
For ongoing updates and discussions surrounding cybersecurity trends, the Cyber Briefing remains an invaluable resource for those keen on enhancing their cybersecurity postures.