
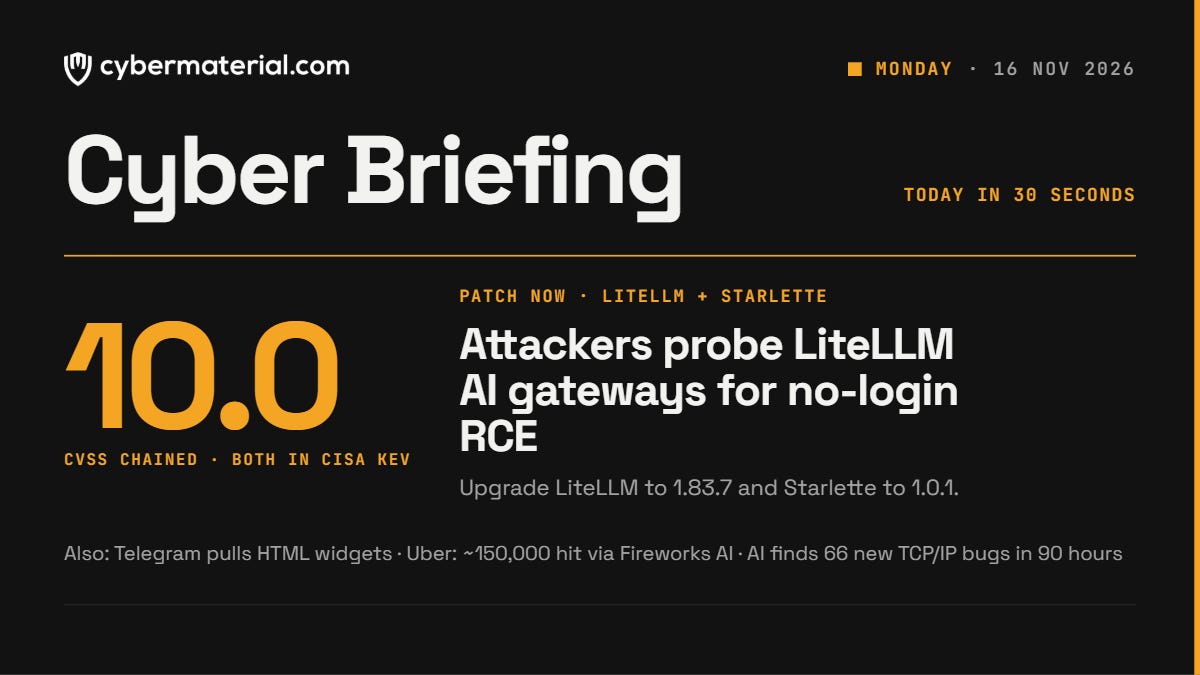


Cybersecurity Briefing Highlights Significant Vulnerabilities and Incidents in the Tech Landscape
In the ever-evolving landscape of cybersecurity, new vulnerabilities and security incidents are emerging regularly, posing threats to organizations and individuals alike. The latest update from Cyber Briefing paints a concerning picture, detailing critical vulnerabilities in popular software frameworks, significant data breaches, and the rapid advancement of AI-driven cybersecurity measures.
Critical Vulnerabilities in LiteLLM and Starlette
This past weekend, cybersecurity experts observed active exploitation of vulnerabilities identified as CVE-2026-42271 and CVE-2026-48710. These vulnerabilities, which affect the LiteLLM framework and Starlette—a widely used Python web framework—present scenarios for unauthenticated remote code execution. The defective Starlette versions fail to properly validate Host headers, enabling attackers to manipulate access controls by injecting malicious characters. As a result, organizations utilizing LiteLLM or any related tools reliant on affected versions of Starlette are urged to upgrade to Starlette version 1.0.1 or later immediately. Additionally, implementing strict hostname validation in web application firewalls is advised to bolster defenses against potential exploits.
Telegram Faces Security Challenges with New Widgets
In another significant incident, Kaspersky reported that Telegram’s newly launched widgets feature is suspected to have been exploited for delivering WebRAT malware. Security researchers recently demonstrated that these widgets could expose other vulnerabilities, enabling remote code execution (RCE). Telegram’s founder, Pavel Durov, has publicly denied these security claims, insisting on the platform’s commitment to user safety. However, experts advise users to exercise caution around the newly released widgets, as potential risks remain.
Uber’s Data Breach Affects 150,000 Individuals
Uber has disclosed a significant data breach affecting approximately 150,000 people, following an unauthorized compromise of a third-party service provider. Stolen data included names, addresses, and driver’s license numbers of those affected. This breach underscores the importance of monitoring personal accounts for suspicious activities and suggests that affected individuals consider placing fraud alerts on their credit reports to protect against identity theft.
AI Accelerates Vulnerability Discovery
On a more optimistic note, advancements in artificial intelligence have considerably increased the speed of vulnerability discovery. Forescout Technologies employed publicly available AI models to identify 99 vulnerabilities, including 66 zero-day flaws, in 10 widely utilized TCP/IP stacks in an astonishing 90 hours. Typically, this level of analysis would take researchers around nine months to complete manually. Despite the significant reductions in time and cost—approximately $935 for static analysis, averaging $2.58 per vulnerability—experts note that the validation process still requires human oversight. Approximately 80 hours of manual verification is necessary, indicating that while AI dramatically enhances vulnerability discovery, it does not replace the need for expert researchers.
Growing Legal Actions Against Universities for Data Breaches
Furthermore, legal actions are emerging as five Boston University alumni have initiated class-action lawsuits against the institution. The lawsuits claim that the university failed to safeguard personal information adequately during a recent data breach involving unauthorized access to its student information system, managed by a third-party contractor. The plaintiffs argue that the university did not provide timely notifications regarding the incident, raising concerns about data protection protocols in educational institutions.
Startup Revolutionizing Customer Relationship Management
In the realm of technological innovation, a promising startup named Dreamteam, founded by former executives from Freshworks, has successfully raised $53 million in seed and Series A funding. The startup aims to revolutionize customer relationship management (CRM) by developing an AI-native CRM solution that automatically captures customer interactions and employs AI agents to handle routine sales tasks. Having signed over 100 customers within three months and replacing traditional solutions like Salesforce and HubSpot at several businesses, Dreamteam is advocating for a fundamental redesign of CRM systems to incorporate AI rather than merely enhancing existing platforms with additional features.
Conclusion
As cybersecurity threats become more intricate and prevalent, organizations must prioritize protecting their systems and data. The emergence of vulnerabilities in widely used frameworks and the potential exploitation of new technologies highlight the need for vigilance, timely updates, and robust security policies. Meanwhile, innovations in AI showcase promising potential in accelerating vulnerability discovery and enhancing cybersecurity measures. In this rapidly changing environment, staying informed and proactive remains critical for users and organizations alike.