


Latest Cybersecurity Developments: A Detailed Overview
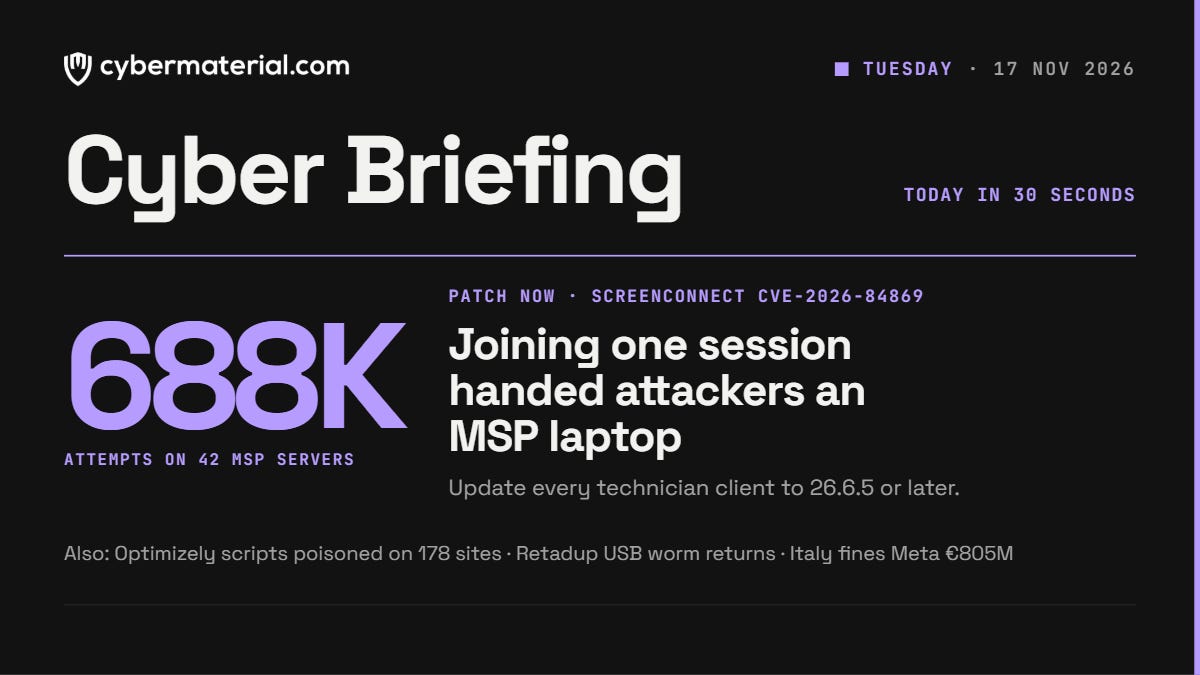
In the ever-evolving landscape of cybersecurity, November 2026 has ushered in crucial updates and alerts that organizations must address to safeguard their digital infrastructures. A recent report from cybersecurity platform Cyber Briefing highlights significant threats, vulnerabilities, and regulatory actions impacting various sectors. Below is a comprehensive overview of key incidents and necessary responses that have emerged recently.
1. Urgent Update for ScreenConnect Users
The necessity for immediate updates within the ConnectWise ScreenConnect platform has become a pressing matter following the identification of a critical vulnerability (CVE-2026-84869) with a CVSS score of 9.9. This vulnerability has been exploited actively to compromise Managed Service Provider (MSP) technician workstations. Huntress, a cybersecurity firm, documented an astonishing 688,000 automated exploitation attempts across 42 MSP servers between October and November 2026. Alarmingly, one successful attack led to the unauthorized takeover of a technician’s laptop merely nine seconds after they joined a remote session.
To mitigate this frightening scenario, all ScreenConnect technician client instances must be promptly updated to version 26.6.5 or later. Moreover, MSPs are encouraged to investigate their systems for any signs of compromise. This includes looking for unauthorized ScreenConnect clients, batch files residing in temporary directories, and unusual entries in startup folders. Failing to act swiftly may expose organizations to further risks, making vigilance and proactive management essential in this case.
2. Code Hijacking at Optimizely
In another industry concern, attackers successfully hijacked Optimizely’s web experimentation platform. This incident resulted in the injection of malicious JavaScript into the websites of 178 organizations, including notable platforms like BBC, CNN, and Zoom. The hack leveraged Optimizely’s JavaScript snippet, used by customers to embed content on their sites, to load harmful scripts from Optimizely’s servers.
Fortunately, Optimizely has acted decisively by patching the vulnerability and ensuring that the malicious code has been removed from affected customer projects. Organizations utilizing the Optimizely platform are advised to review their website integrations and ensure that security measures align with best practices to prevent future occurrences.
3. Resurgence of the Retadup USB Worm
Cybersecurity researchers at Kaspersky have identified a new variant of the Retadup USB worm, which first came to light in 2019. This renewal of threat activity sees the worm facilitating additional malware deliveries, specifically through a variant known as CoffeeLoader. Kaspersky reported that they have successfully blocked attempts from this worm on approximately 15,000 systems this year alone.
Organizations are urged to stay vigilant by monitoring their systems for unusual activity associated with the rundll32.exe process. Recognizing suspicious DLL files in temporary directories can also serve as a crucial indicator of potential infection.
4. Italy’s Regulatory Action Against Meta
In significant regulatory news, Italy’s data protection authority levied a staggering fine of €805 million against Meta. The fine stems from the company’s Facebook app gaining unauthorized access to users’ entire photo galleries via a vague permission request associated with the app’s photo suggestions feature. This permission was found to be insufficiently transparent, as it allowed Meta to scan users’ entire camera rolls without explicit consent.
Meta now faces a mandate to request separate, explicit consent for this feature, turn it off by default, and provide clear explanations regarding data usage. Failure to comply with these new regulations could result in further restrictions and scrutiny.
5. Enhanced Data Control in macOS
On a positive note, Apple has rolled out new permission controls with the beta release of macOS 15.3, providing users with enhanced oversight regarding what data applications can access. This update particularly targets AI agent applications, allowing users to receive detailed insights into the data requests made by apps prior to granting access. Such transparency is crucial for mitigating potential security breaches, especially in environments increasingly reliant on AI technologies.
6. AI-Powered Vulnerability Audits by GitHub
In a progressive move, GitHub’s security research team has begun utilizing AI agents to conduct software vulnerability audits, initially targeting authentication and authorization bugs. The innovative approach combines machine intelligence with human oversight, as every report generated by the AI undergoes thorough human review. This dual methodology aims to eliminate false positives before communicating findings to software maintainers, optimizing the performance of the agents in identifying security flaws.
Conclusion
These developments underscore the ongoing challenges and advancements in the field of cybersecurity. Organizations must remain proactive in addressing vulnerabilities while adapting to new threats, regulatory requirements, and technological innovations. The insights provided here serve as both a warning and a guide for stakeholders across various sectors to enhance their cybersecurity postures in a challenging digital landscape.