
Cybersecurity Update: Key Vulnerabilities and Scams on the Rise
In a landscape increasingly dominated by technology, the cybersecurity field remains vigilant against emerging threats. Recent advisories highlight the critical nature of several security vulnerabilities, alongside the rise of sophisticated scams that leverage artificial intelligence. The latest updates reflect these pressing challenges, with insights into significant incidents affecting organizations and individuals alike.
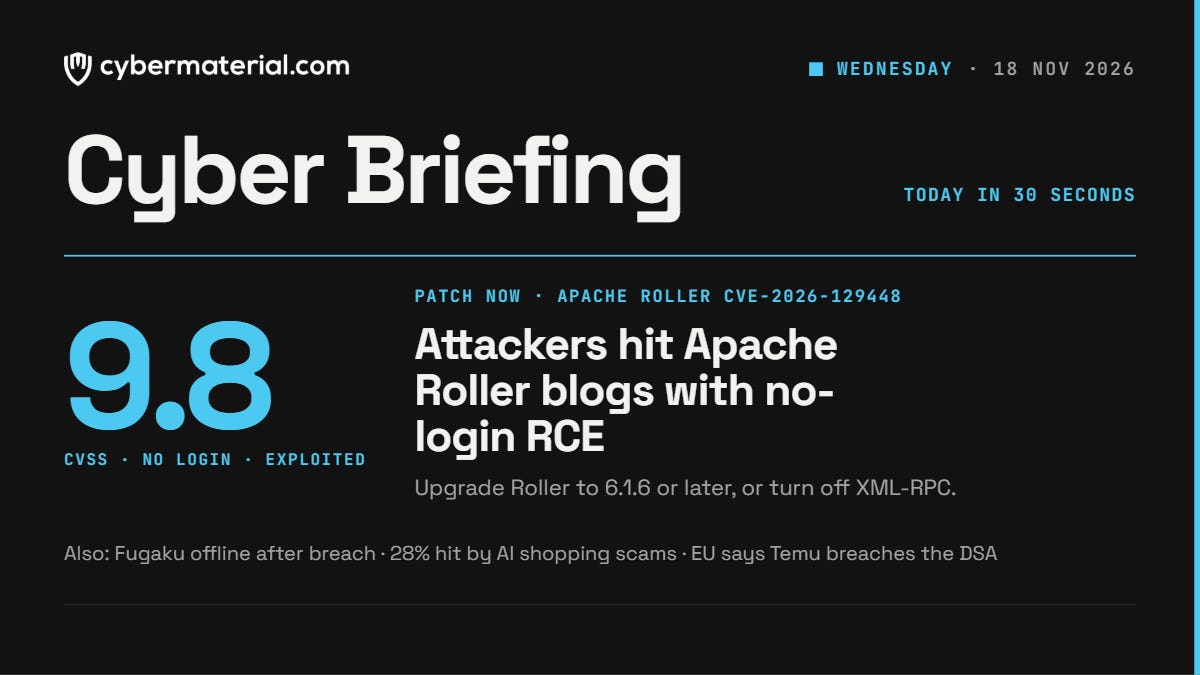
One of the most urgent warnings comes from Apache, which has issued a prompt recommendation for all users of Apache Roller to patch their systems against a critical vulnerability recognized as CVE-2026-129448. This flaw, rated 9.8 on the CVSS scale, allows attackers to seize control of servers without requiring any form of authentication. Exploit attempts are already reported in the wild, prompting Apache to advise users to upgrade to version 6.1.6 or later immediately. Alternatively, disabling XML-RPC in web.xml has been proposed as a temporary measure to mitigate risk. This situation underscores the need for proactive measures in maintaining software security.
Turning attention to Japan, a distressing breach at the RIKEN research institute has led to the temporary shutdown of the renowned Fugaku supercomputer. This powerful machine, celebrated for its computational prowess, was compromised, resulting in unauthorized access to details of 4,222 users, including sensitive SSH keys. The breach has forced RIKEN to instruct all individuals with accounts to revoke and replace their keys as a precautionary measure. As the situation develops, it remains unclear if any research data has been illicitly accessed or exported. The incident raises alarms about the security vulnerabilities that can target even the most advanced computing facilities.
In a related concern, a recent survey by Malwarebytes has revealed an alarming trend: 28% of consumers reported experiencing AI-related scams in the past year. Notably, younger shoppers in the Gen Z demographic appear particularly vulnerable, with 42% indicating they have encountered such scams. These cybercriminals exploit sophisticated techniques to craft convincing fake shopping websites and product images, often impersonating major retailers. Amazon has emerged as a frequent target for impersonation attempts. Fraudulent communication methods such as personalized messages and fake delivery notifications are often employed to extract payment information and personal data from unsuspecting consumers. As online shopping intensifies with the holiday season approaching, the need for consumer awareness is paramount.
The regulatory environment has also entered the spotlight, particularly with the European Commission’s preliminary findings against the Chinese e-commerce platform Temu. The platform allegedly fails to comply with the Digital Services Act by not adequately preventing the sale of unsafe products. Identified compliance issues include inadequate moderation, insufficient product testing, and weak enforcement against repeat offenders. Temu now faces substantial penalties, including fines of up to 6% of its global turnover, which could significantly impact its operational future. The EU’s firm stance illustrates the ongoing effort to ensure e-commerce platforms prioritize consumer safety.
On another front, OpenAI has made waves with the release of two new AI models: GPT-6.2 Astra and GPT-6.2 Sol, targeting complex professional tasks and everyday workflows, respectively. The models are available for Plus, Enterprise, Pro, and Edu subscribers, accessible via popular services such as ChatGPT Work and Codex. With enhanced performance metrics and a 20% reduction in API costs, OpenAI aims to cater to a responsive market while implementing safety frameworks to monitor AI outputs. The company’s proactive approach reflects the dual-use challenges associated with rapidly advancing technology.
Amidst these developments, a new secure messaging app called Germ DM has made its debut on Android platforms, following its earlier launch on iOS. Founded by former Stanford lecturer Tessa Brown and ex-Apple iMessage engineer Mark Xue, Germ DM introduces innovative features such as “burner cards.” These cards create separate identities within the app, enabling users to share various personas with different contacts without linking to their phone numbers. By employing advanced encryption protocols, Germ DM aims to set a high standard for digital privacy in an age where personal data is increasingly at risk.
As the cybersecurity landscape evolves, vigilance becomes ever more crucial. Organizations and consumers alike must stay informed and engage with security resources to safeguard against the myriad threats that pervade the digital world. With proactive measures and a commitment to continuous education, stakeholders can work collaboratively to mitigate risks and fortify defenses against ever-evolving cyber challenges.