


Cybersecurity Briefing: Key Updates and Incidents
In cybersecurity news this week, several significant incidents have come to light, affecting major companies and institutions across different sectors. The vulnerabilities in systems and data breaches highlight the need for increased vigilance and strategic action among organizations to protect sensitive information.
NGINX Vulnerabilities Require Immediate Action
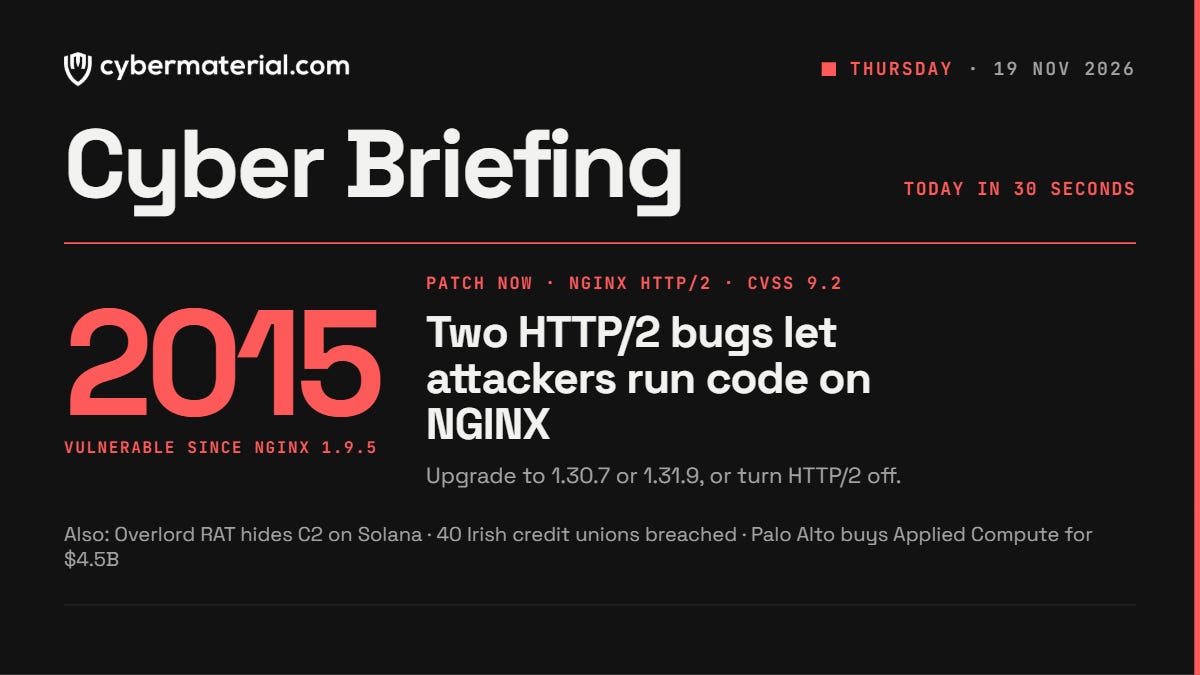
F5 Networks has recently addressed two critical flaws in NGINX’s HTTP/2 implementation that could allow unauthorized attackers to execute code remotely. The vulnerabilities, with a CVSS score of 9.2, were identified in both the Open Source and Plus versions of NGINX, necessitating immediate updates to versions 1.30.7 or 1.31.9. Organizations still using affected versions are advised to either install the necessary patches or disable HTTP/2 until they can conduct a proper update to safeguard their systems.
This update is crucial, considering one of the vulnerabilities has existed since 2015, underscoring the importance of staying current with security patches.
Espionage Charges Against a Russian National
In related news, a Russian individual identified as Igor Andreevich D’iu has been charged in the United States for allegedly engaging in espionage against Palantir Technologies, a prominent defense technology firm. D’iu was reportedly recruited via Telegram and tasked with stalking employees, even photographing their computer screens. This case illustrates a broader trend of Russian intelligence agencies intensifying their efforts to infiltrate U.S. defense contractors through social media and other platforms. Defense sectors are urged to reevaluate their security measures and reinforce employee training in identifying potential espionage tactics.
Significant Data Breach Involving Irish Credit Unions
A cyberattack on Wellington IT has resulted in the exposure of saved payee data for around 40 Irish credit unions, impacting approximately a quarter of the nation’s credit union landscape. The breach, which took place over several days in early October, allowed unauthorized access to sensitive information such as payee names, International Bank Account Numbers (IBANs), and Bank Identifier Codes (BICs). However, it’s important to note that access credentials and passwords were not compromised.
Criticism has emerged directed at Wellington IT for the delayed notification to affected credit unions, many of whom only learned of the breach recently, despite the flaw being corrected by October 6. Ireland’s Minister for Credit Unions has expressed concern about the protracted timeline for informing institutions, which is vital for maintaining customer trust.
Palo Alto Networks Acquires Applied Compute
In a strategic move, Palo Alto Networks announced an agreement to acquire Applied Compute for $4.5 billion in stock. The acquisition aims to bolster Palo Alto’s capabilities in training and deploying open-weight artificial intelligence models for enterprise clients. The completion of this deal is anticipated between February and April of 2027. Following the transaction, Applied Compute’s research team and platform will integrate into Palo Alto’s existing offerings. Furthermore, CEO Yash Patil will take on the role of co-chief AI officer, positioning the company to expand its GPU compute capacity significantly—targeting over 100 megawatts within three to five years.
Emerging Threats from North Korean Actors
Cisco Talos researchers have identified a financially motivated threat group, tentatively linked to North Korea, dubbed UAT-12643. This group has been employing blockchain-based command-and-control (C2) infrastructure to target various online sectors, including cryptocurrency holders, gaming enthusiasts, and VoIP users predominantly located in Europe. The group utilizes a sophisticated approach, embedding encrypted C2 server URLs within Solana blockchain transactions. They deploy advanced malware such as the Overlord remote access trojan (RAT), alongside other tools designed to abuse cryptocurrency-related transactions.
Organizations are encouraged to be vigilant and monitor for related suspicious activities, including certain types of files and unusual modifications within systems.
Governance Gaps in Open-Weight AI Models
The rapid adoption of open-weight AI models has raised concerns regarding governance and compliance. While these models are lauded for their cost-effectiveness and greater control, the associated risks necessitate a robust governance framework. Security teams must pivot towards establishing clear policies and protocols, focusing on model provenance, usage tracking, and risk assessment before deploying these models in essential production environments.
Conclusion
As the cybersecurity landscape continues to evolve, recent incidents demonstrate the pressing need for organizations to remain proactive. Whether addressing software vulnerabilities, tackling espionage threats, or negotiating acquisitions with long-term growth in mind, comprehensive strategies are essential to maintain a robust security posture in today’s increasingly complex digital environment. Organizations are urged to enhance their cybersecurity frameworks, ensuring protection from both external threats and internal vulnerabilities.