
Cybersecurity Updates: Key Alerts and Incidents You Should Know
In an ever-evolving landscape of cybersecurity threats, the latest updates from various tech giants and security researchers serve as crucial reminders of the risks and vulnerabilities that exist. This week’s Cyber Briefing highlights several significant incidents and advisories, emphasizing the need for vigilance and prompt action in securing digital assets.
Recent Vulnerabilities and Recommendations
Critical Update for Pillow Library
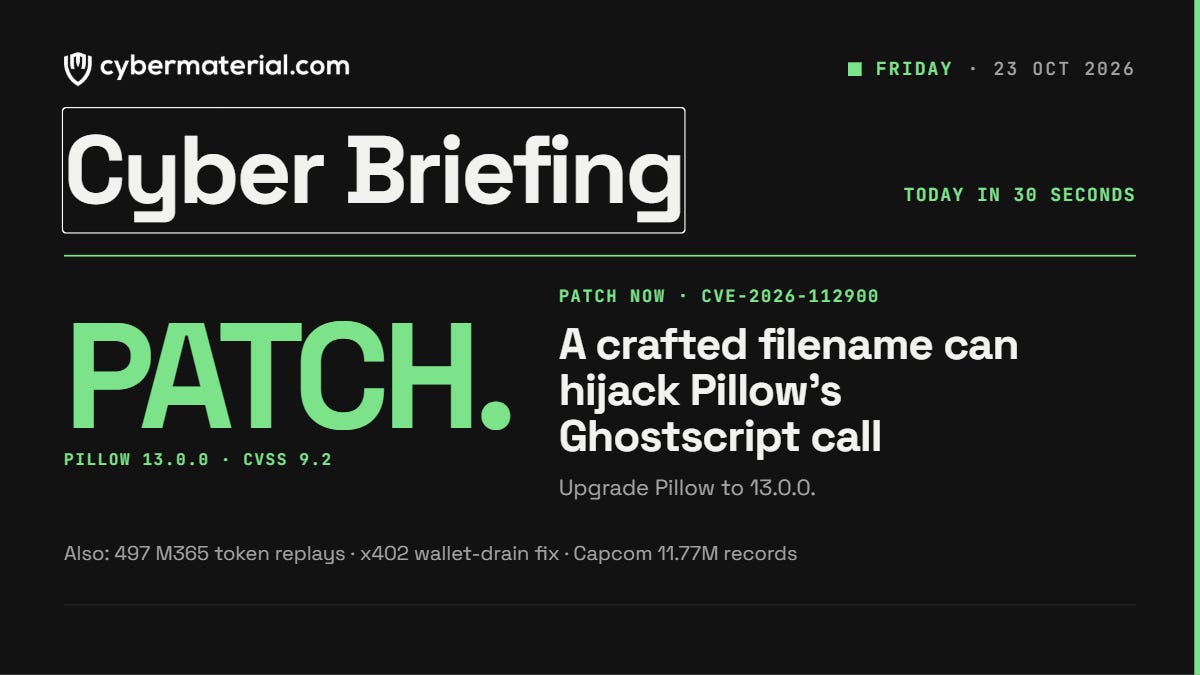
A pivotal issue has emerged with the Pillow library, a widely used tool in Python for image processing. Version 2.6.0 to 12.3.0 were found to have a serious vulnerability designated as CVE-2026-112900. This vulnerability allows an attacker to manipulate a crafted filename to inject arguments into Ghostscript, which could potentially lead to Remote Code Execution (RCE). The newly released version 13.0.0, rolled out on October 16, 2026, rectifies this flaw, transforming its CVSS score from a critical 9.2 to a medium risk rating according to Pillow’s own release notes.
For developers and organizations that utilize Pillow in their applications, immediate action is advised: patch the Pillow library in all Python applications and servers where Ghostscript is installed. It’s significant to note that while the vulnerability has been documented, no reports indicate exploitation in the wild as of yet.
Microsoft 365 Targeted by Token-Spraying Campaign
In a comprehensive cybersecurity investigation, Huntress identified a widespread business email compromise campaign that resulted in over 200,000 login attempts targeting Microsoft 365 environments globally from July to September 2024. Successfully, 497 of these attacks compromised accounts. Utilizing advanced adversary-in-the-middle techniques, attackers bypassed established multi-factor authentication safeguards by stealing session tokens.
Organizations are urged to implement Conditional Access Policies that require MFA for all users and cloud applications. In cases of suspected compromise, organizations must promptly revoke sessions, reset passwords, and conduct thorough audits of device registrations.
x402 SDK Flaw Exposed Critical Vulnerability
A significant vulnerability has been found in the x402 Software Development Kits (SDKs), whereby malicious APIs could drain the entirety of funds from AI agent token balances that automatically sign payment transactions. This flaw, which received critical attention, existed because the SDK did not enforce any spending limits until patches were introduced on August 18, revealing just how crucial it is to regularly update security measures in software development.
Data Breach: Capcom Exposes Millions of Records
In a concerning development, Capcom disclosed that unauthorized access to its systems had exposed 11,774,247 CAPCOM ID records. This breach included sensitive information such as email addresses, account creation times, last login details, and IP addresses, among other personal data. Notably, 43 records were compromised, revealing even more personal details such as date of birth and country of origin. Although Capcom has confirmed the compromise of these records, they guarantee that customers’ passwords, which were set by users, remain secure, and no credit card information was affected. Capcom detected this breach on October 19 and reported it to local authorities two days later.
AI and Cybersecurity: New Guidelines from Deloitte
Addressing the rapidly advancing field of artificial intelligence in cybersecurity, Deloitte has published new guidelines emphasizing the necessity for securing AI agents within enterprise environments. The report illustrates the importance of treating each AI agent as an individual digital identity, complete with clear permissions and ownership parameters. Deloitte advocates for a meticulous balance between automated detection capabilities and human oversight, recommending that while routine actions should adhere to established limits, significant decisions should necessitate human approval. The establishment of an AI control framework is also recommended, which would oversee agent behavior, enforce access restrictions, and enable real-time interruptions of harmful actions.
Legislative Developments in the UK
In a legislative shift, the UK government has proposed a new framework intending to modernize laws established in 1885 that protect subsea cables. This proposal seeks to instill robust penalties of up to 14 years imprisonment for individuals intentionally damaging critical underwater infrastructure. The necessity for such measures emerged after recent observations of Russian submarine operations, while the majority of cable damage incidents are noted to stem from fishing vessels and dragging anchors. The legislation includes imposing new security obligations for telecom operators, alongside empowering ministers to initiate protective measures.
Conclusion
As this week’s Cyber Briefing reveals, the cybersecurity landscape is rife with new vulnerabilities and evolving threats. The significant updates, from software vulnerabilities in widely used libraries to major data breaches and emerging AI guidelines, underline the importance of proactive measures in safeguarding digital environments. Organizations must stay informed and act promptly to mitigate risks associated with these threats. It is advisable for all stakeholders to remain vigilant, continuously assessing their security protocols in light of the evolving cyber threat landscape.