


Cybersecurity Briefing: Key Developments From October 27, 2026
On October 27, 2026, significant cybersecurity updates were released by notable organizations, impacting various sectors and highlighting the ongoing struggles against cyber threats. The information outlines critical vulnerabilities, cyber intrusions targeting major companies, and the implementation of new defensive tools in the fight against these pervasive threats.
Critical Vulnerability in Veeam Software
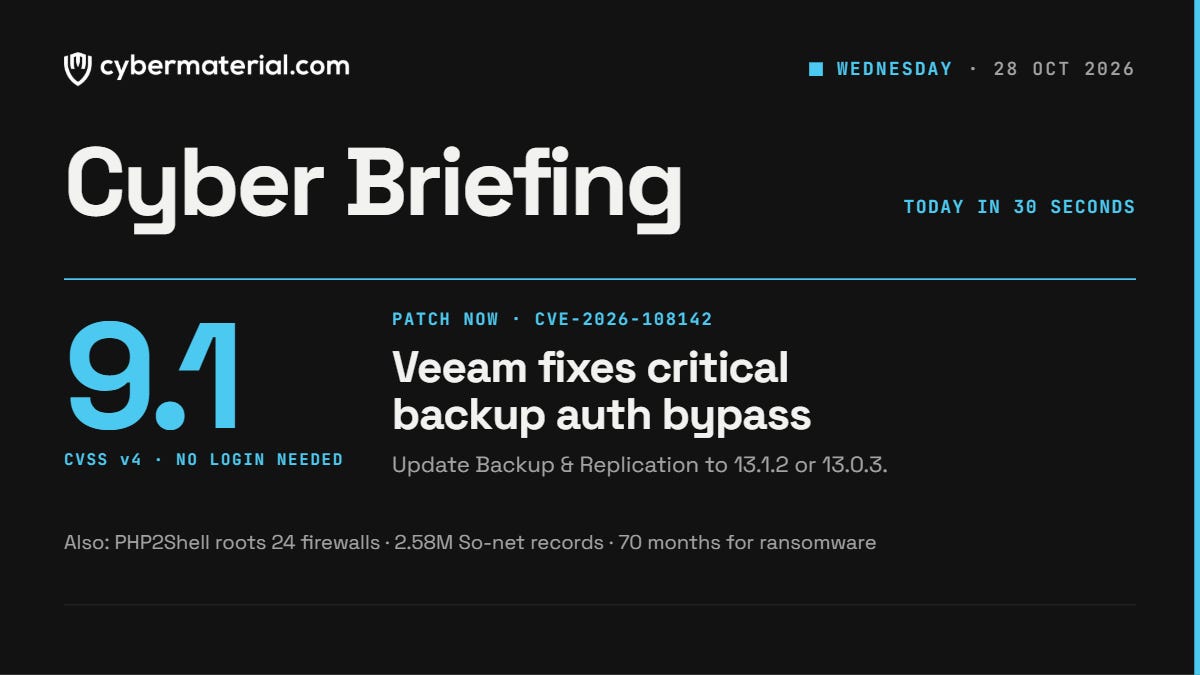
Veeam announced a pivotal patch for a critical security vulnerability identified as CVE-2026-108142. Rated with a CVSS score of 9.1, this flaw allows unauthenticated attackers on the network to bypass authorization in the CDP Coordinator Service of the Backup & Replication software. The affected versions include 13.1.1.18 and earlier, as well as version 13.0.2.29 and earlier; it should be noted that version 12.x remains unaffected. The advisory also addressed two medium-severity path traversal vulnerabilities and a significant local privilege escalation defect found in the managed Veeam Agent for Linux. This patch underscores the necessity for organizations reliant on Veeam’s services to update promptly to maintain security integrity.
PHP2Shell Exploit Targeting Firewalls
In another alarming development, a security firm named Dream reported a sophisticated cyberattack linked to a group suspected to have ties to China. The attackers exploited two PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) in combination with a Linux kernel privilege escalation flaw (CVE-2026-46300). This malicious chain resulted in a root webshell being placed on 24 internet-facing firewalls located in the United States, Japan, Taiwan, and South Korea. Notably, the breach extended into a US government-affiliated organization, compromising its internal firewall management server and exposing sensitive configurations as well as credentials. Despite the speculated connections to Chinese-language prompts observed during the attack, further verification remains necessary to ascertain the involved group.
Sony Confirms Data Breach
Substantial security concerns also emerged when Sony Network Communications disclosed a breach affecting its So-net member database. The incident, which occurred on October 19, exposed an astonishing 2,585,481 records, comprised of personal details such as names, phone numbers, email addresses, and user IDs. An additional leak included passwords associated with 54,401 email addresses and 16 bank account details. Fortunately, membership login passwords and credit card numbers were reported to be secure. This breach highlights the vulnerabilities in data handling by large corporations and the potential ramifications for millions of users.
Sentencing in Ransomware Case
In legal developments, 36-year-old Artem Stryzhak, a Ukrainian implicated in international ransomware attacks, was sentenced to 70 months in prison. These attacks were linked to damages estimated at approximately $100 million, affecting various sectors including hospitals, government entities, and law firms globally. This case serves as a stark reminder of the imperative for organizations to reassess their ransomware defenses and ensure robust incident response plans are in place to mitigate future risks.
Cisco Introduces an AI Behavior Detection Tool
Cisco’s recent unveiling of Project Quarry marks a significant advancement in cybersecurity tools. This open-source behavior detection engine focuses on monitoring AI agent behaviors by analyzing sequences of actions, rather than isolated incidents. The initiative arises from security incidents like the Hugging Face breach, emphasizing the critical need for advanced monitoring systems. Organizations can utilize Quarry to establish rules that flag suspicious actions, thus augmenting traditional security measures and improving response protocols.
Innovative Vulnerability Management by Black Duck
Amplifying the conversation around vulnerability management is Black Duck’s launch of Signal Agentic Fix, an innovative AI tool designed to streamline the vulnerability remediation process. This tool automates the journey from identifying vulnerabilities to validated fix submission. By leveraging deterministic approaches and AI for triaging and generating fixes, organizations can close the gap between discovery and remediation effectively. This solution can complement developer AI agents or be integrated directly into DevOps workflows with appropriate oversight mechanisms.
As cyber threats continue to evolve, the news from October 27, 2026, serves as a critical reminder for organizations to remain vigilant and proactive. The ongoing developments in cybersecurity showcase the increasingly sophisticated tactics employed by attackers and the essential measures needed to protect sensitive data across all sectors. Organizations are urged to remain informed and take necessary actions to safeguard their infrastructure and data assets.