
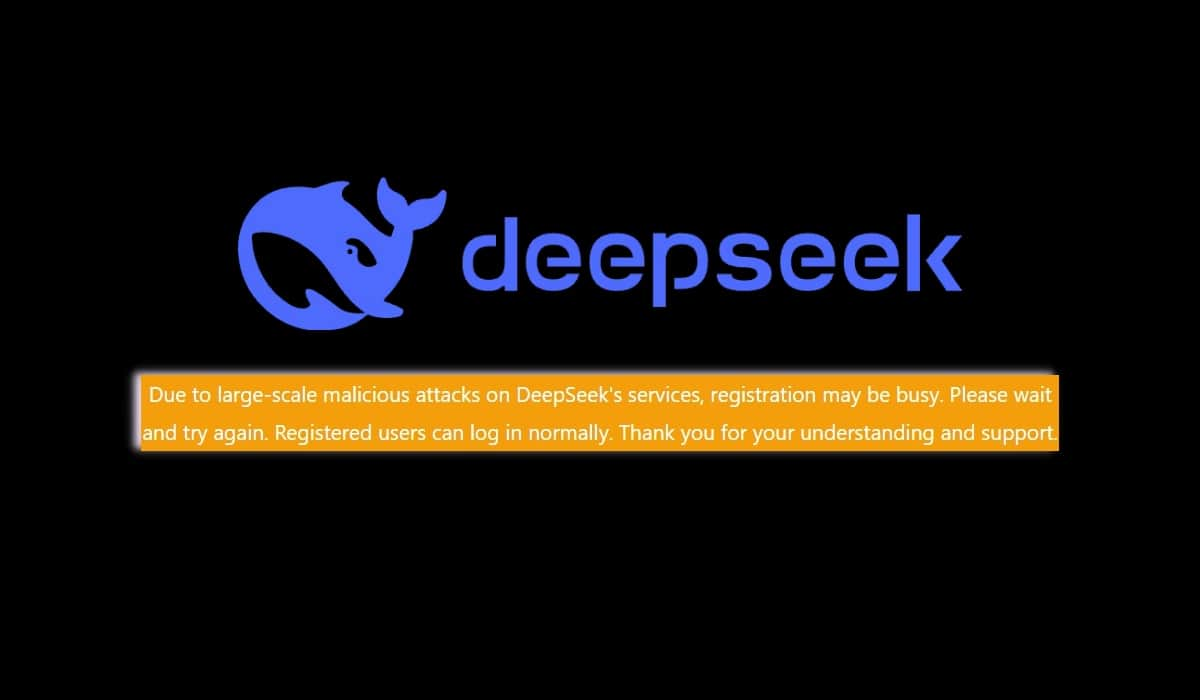


DeepSeek, the China-backed AI platform that has been making waves in the industry, is currently facing a major cyberattack that has disrupted new user registrations. The company acknowledged the issue in a statement on its website, alerting users that registration may be affected due to the ongoing malicious attacks. Despite the challenges, DeepSeek assured existing users that they can still log in and use the platform as usual.
The rise of DeepSeek as a prominent player in the AI world has been swift and impressive. The platform, known for its intuitive features and user-friendly interface, quickly gained popularity, even surpassing established competitors like OpenAI’s ChatGPT in the free application section of Apple’s App Store in the United States. This rapid ascent to the top has put DeepSeek in the spotlight, drawing the attention of millions of users worldwide.
However, with great success comes great risk, as illustrated by the recent cyberattack targeting DeepSeek. The attack primarily affected new user registrations, preventing potential users from signing up for the platform. Cybersecurity experts have emphasized the importance of bolstering defenses, especially for rapidly growing platforms like DeepSeek, which can become prime targets for cybercriminals seeking to exploit vulnerabilities.
Jake Moore, a Global Cyber Security Advisor at ESET, highlighted the potential dangers inherent in DeepSeek’s sudden popularity: “DeepSeek has certainly been in the limelight in recent days, which can act as a huge honeypot for cybercriminals. This is typical for any new platform which contentiously dominates the media for multiple reasons and can attract multiple groups of threat actors looking for any potential vulnerability to exploit.”
As DeepSeek works to address the cyberattack and mitigate its impact on new user registrations, the incident serves as a stark reminder of the growing pains that often accompany rapid success. New platforms experiencing exponential growth must be vigilant about cybersecurity measures to protect their users and data from malicious actors.
The ongoing situation with DeepSeek is still developing, and users are encouraged to stay informed as the company navigates this cybersecurity challenge. In the ever-evolving landscape of digital threats and attacks, the importance of robust cybersecurity practices cannot be overstated.
As the story unfolds, cybersecurity experts continue to monitor the situation closely, emphasizing the critical need for proactive measures to safeguard against future cyber threats. Stay tuned for updates on DeepSeek’s response to this cyberattack and the steps being taken to ensure the security of its platform and users.