


Emergence of Exvicy Malware-as-a-Service Platform Targeting WordPress Sites
A recently unveiled Malware-as-a-Service platform known as Exvicy is reportedly exploiting compromised WordPress websites to disseminate malicious ClickFix lures while masquerading as Cloudflare Turnstile verification pages. This new threat poses significant risks to both website owners and users, as it employs techniques designed to bypass standard security measures.
Researchers at Sekoia have expressed a high degree of confidence in their findings, identifying Exvicy as a clone of the already infamous ErrTraffic framework. The new platform notably reuses elements such as JavaScript injection logic, fake-verification code, and command-and-control (C2) communication routines that have been integral to ErrTraffic’s function. The actor behind Exvicy initially offered access to the service at a monthly rate of $1,200, later increasing the price to $2,000 in August. This price hike appears to reflect claims regarding an uptick in detection pressure, necessitating continual updates and enhancements to the malware.
The Exvicy offering is comprehensive, featuring an administration panel alongside JavaScript tools engineered to convert compromised websites into effective malware delivery mechanisms. The research team from Sekoia traced the origins of Exvicy back to a screenshot shared in a related sales thread. This image presented part of the Exvicy administration panel alongside a partially concealed domain under Cloudflare’s management.
By analyzing the visible DNS configuration and the timing of domain registrations, researchers successfully pinpointed several domains associated with the Exvicy operator, which include us-addnewdevice[.]com, cloudflarecapcha[.]com, perfectverified[.]com, newsecuredevice[.]com, and unitedstateverif[.]com. These domains facilitate the operation’s infrastructure, hosting Exvicy panel pages, PowerShell payloads, and fake Cloudflare verification content.
Sekoia’s investigations have revealed a downloader specifically hosted through identified infrastructure, capable of retrieving an MSI payload from a Cloudflare R2 bucket. Observations indicated that, in one case, this installer managed to deploy the legitimate PuTTY SSH client, suggesting that the Exvicy framework is adaptable for disseminating arbitrary payloads rather than remaining confined to a specific malware family.
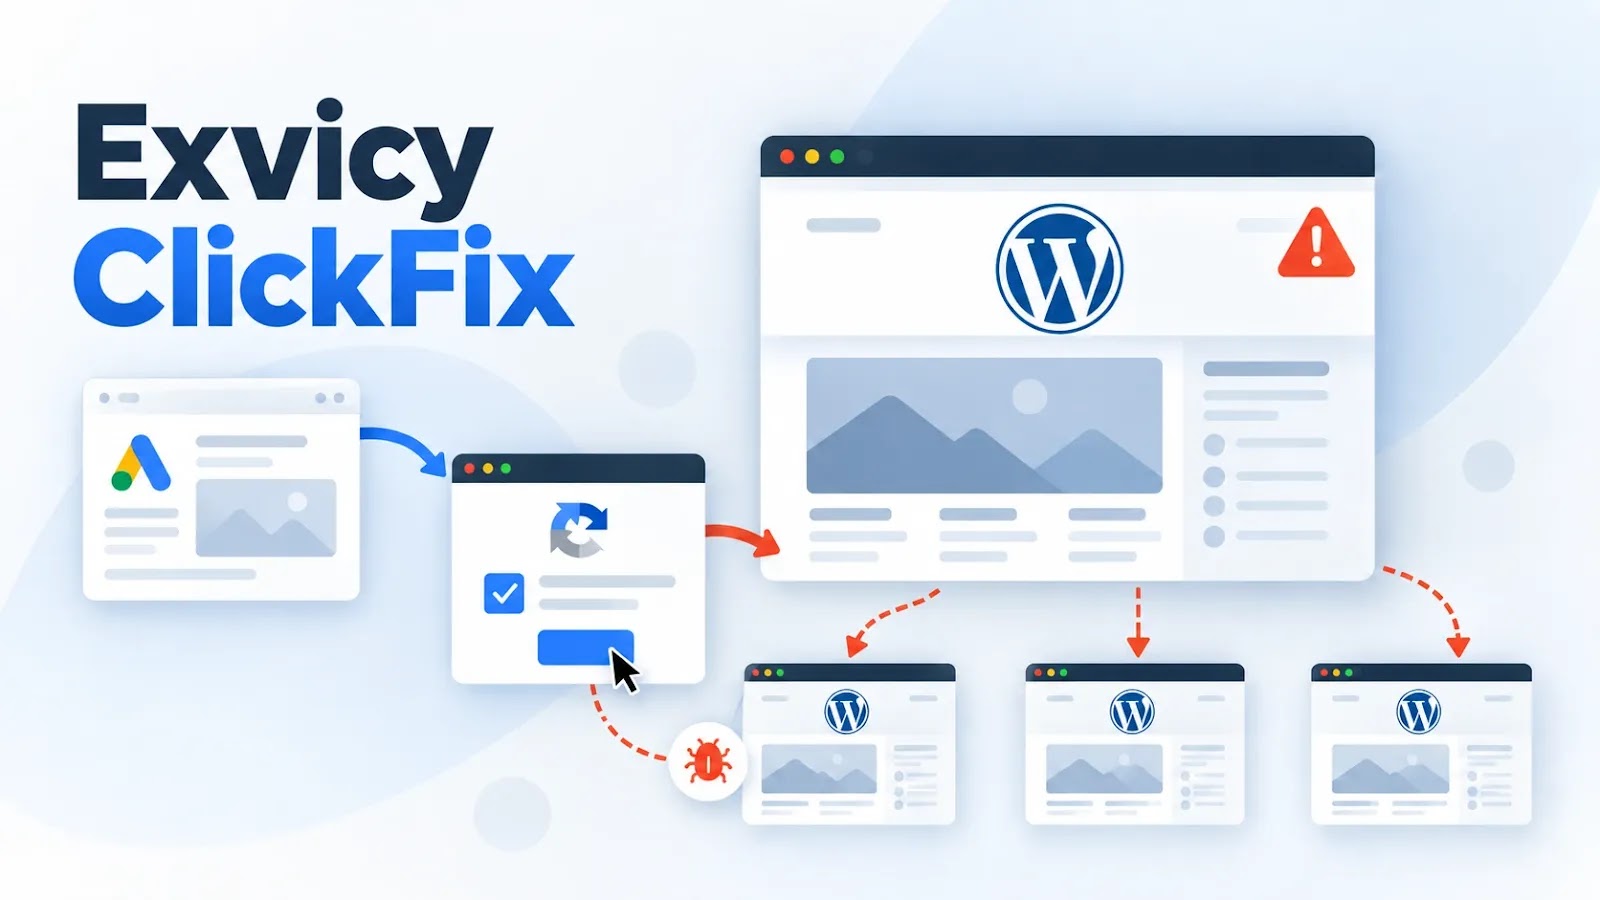
The infection cycle instigated by Exvicy begins with the injection of an obfuscated JavaScript snippet into a compromised WordPress site. This code employs Base64 encoding, XOR encryption, and randomized variable names to obstruct inspection efforts. Once this code is decoded within a visitor’s browser, it creates a full-screen iframe labeled “Security Check,” facilitating contact with Exvicy’s infrastructure to load the subsequent ClickFix page.
This generated lure impersonates a Cloudflare Turnstile CAPTCHA, designed not to exploit a browser vulnerability but rather to trick victims into unwittingly allowing the infection. The lure prompts users to engage in specific keystrokes—pressing “Win+R,” copying content to the clipboard with “Ctrl+V,” and finally hitting Enter. Such actions initiate the Windows Run dialog, which serves as the entry point for executing commands provided by the attackers. Notably, Exvicy has adopted a multilingual approach, offering instructions in 13 languages to widen its campaign’s reach across various regional targets.
Once triggered, the malware payload retrieves an additional remote PowerShell script for execution. Sekoia documented C2 communications that record potential victims, gather telemetry about their browser and operating system, track interactions with the fake CAPTCHA, and confirm whether a victim has executed the harmful command. The platform also tracks visit events and user interactions, allowing affiliates to monitor conversion performance effectively.
While Exvicy has made claims to differentiate itself from ErrTraffic by employing Win+R shortcuts as opposed to Win+X, Sekoia’s analysis indicates that both platforms share a far more substantial amount of code. This includes identical functions for UUID generation and clipboard manipulation, translation support, anti-analysis checks, C2 request routines, and status-polling workflows. A significant divergence arises in how the two frameworks handle their C2 infrastructure: ErrTraffic relies on EtherHiding to store C2 information in blockchain smart contracts, whereas Exvicy hardcodes its C2 servers directly into the injected script.
Exvicy first surfaced on the Russian-speaking Exploit.IN cybercrime forum on May 26, 2026, by an operator using the handle @Exvicy. Sekoia’s telemetry further indicates that multiple customer environments have been observed communicating with Exvicy’s C2 servers, validating the operational status of this new service.
To counter this emerging threat, defenders are advised to monitor WordPress installations closely for unexpected JavaScript injections, suspicious outbound browser requests to verification domains, and clipboard-triggered PowerShell executions. Additionally, organizations should educate users on legitimate CAPTCHA procedures, emphasizing that no credible service requests actions that involve using the Run command or executing PowerShell commands.
Indicators of Compromise (IOCs)
Researchers have traced various suspicious domains, providing a crucial resource for cybersecurity teams. The following domains have been linked to this emerging threat:
- kawaiininjaclub[.]cfd
- jouncepopdownloadnow[.]com
- jumppopdownloadsecret[.]monster
- lastdayornot[.]top
- searlepub[.]com
- whirlpoploaderfast[.]com
These domains serve as early indicators of possible compromise, with specific "first seen" dates in August 2026. As cybersecurity professionals continue to monitor the landscape, awareness of these IOCs can greatly enhance an organization’s ability to respond to this burgeoning threat effectively.
In conclusion, the advent of Exvicy signifies a growing sophistication in malware distribution tactics, underscoring the need for vigilant monitoring and robust user education to mitigate risks associated with compromised digital environments.