
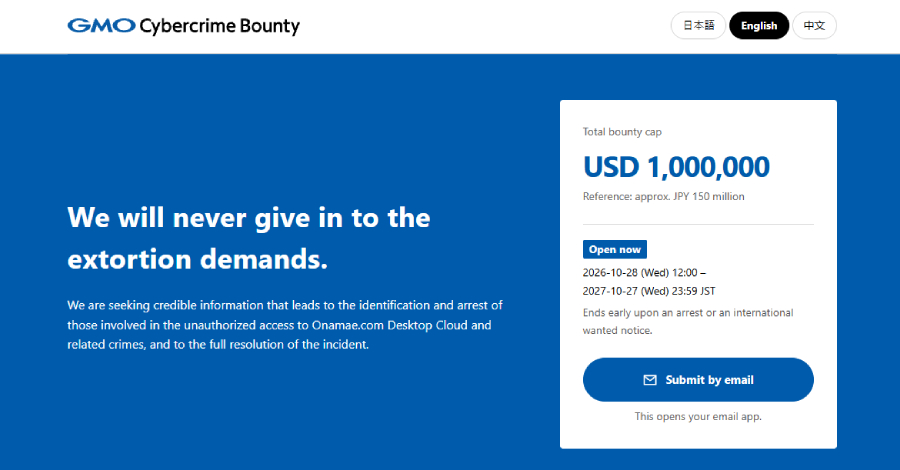


Japan’s GMO Internet Group recently announced a significant initiative aimed at addressing a severe cybersecurity breach that compromised its Onamae.com Desktop Cloud service. Following a refusal to meet an extortion demand, the company has introduced a reward program that offers up to $1 million for tips leading to the capture of the hackers involved in the incident. This program, launched on October 28, signals GMO’s determination to combat cybercrime effectively.
The breach, which came to light on October 20, prompted immediate action from GMO as it discovered that malicious software had been installed on various customer servers. The company swiftly shut down all affected servers across its plans, comprising over 26,739 potentially compromised systems. Notably, these servers hosted Windows desktops used predominantly for foreign exchange (FX) trading, which raises significant concerns regarding financial security among affected users.
As the situation unfolded, GMO encountered a stark ultimatum. The attackers, presumed to be behind the breach, demanded approximately $50 million (equivalent to around ¥8 billion) on October 21. They further threatened customers by claiming they could manipulate trading accounts and potentially publicize sensitive data linked to both the service and its users. On October 27, the perpetrators took their threats further by posting alleged customer information on their website. In a tactical response, GMO’s domain and mirror sites were shut down around 4 a.m. Japan time on October 28, with plans to counter any emerging sites designed to disseminate stolen information.
Understanding the Reward Program
The newly established program, dubbed the GMO Cybercrime Bounty, is exclusively funded by the GMO Internet Group. Tips can be submitted anonymously in various languages via a dedicated website. However, rewards will only be disbursed if the information provided leads directly to an arrest or an international wanted notice—such as an Interpol Red Notice. Participants are invited to share any details linking individuals or digital assets to the breaches or extortion attempts, emphasizing the need for substantiated evidence rather than conjecture or public information.
The tipping system is structured to ensure that rewards are awarded based on the level of assistance the information provides towards law enforcement actions. Importantly, any tipster must verify their identity before receiving payment. The program is set to remain active until either an arrest is made, an international notice is issued, or until October 27, 2027—whichever occurs first.
There are strict guidelines outlining who can and cannot receive rewards. Individuals directly involved in the crime or those who obtained information through illegal means, including purchasing leaked data, will be excluded from the program. Additionally, GMO has reminded potential informants not to engage in illegal activities or negotiate with the attackers themselves.
Implications of the Breach
The implications of this breach extend well beyond security concerns for GMO. Numerous customers have reported unauthorized trades occurring on their accounts since October 21, raising significant alarms in the financial community. Brokers, like OANDA Japan, confirmed that third parties accessed and traded on some of their clients’ accounts using login information believed to have been stolen from GMO’s compromised servers. Consequently, OANDA has taken precautionary measures by restricting trading on affected accounts.
Simultaneously, FXTF has issued warnings about potential theft of logins from customers utilizing Virtual Private Servers (VPS). In light of these unsettling developments, both companies have advised their customers to promptly change passwords and monitor their trading activities diligently.
Despite the chaos stemming from the breach, GMO Internet Group has articulated its commitment to addressing the repercussions diligently. The company plans to compensate each current user with ¥5,000 and cover verified losses arising from unauthorized transactions linked to the breach. Customers whose information has been confirmed as leaked will receive additional remuneration based on the nature of what was compromised.
Future Steps and Customer Guidance
In terms of immediate actions for customers, GMO has issued a series of recommendations. This includes changing trading account passwords from a secure device, ending all active sessions, and turning on two-factor authentication where available. Moreover, customers are advised to conduct virus scans on their devices, back up important data, and refrain from engaging with any individuals claiming to be involved in the attack.
Looking ahead, GMO has declared that it will not resume services on the compromised systems in their current state. Instead, customers seeking Windows desktops will be offered migration to an alternate service, complimentary for six months, contingent on their agreement.
The proactive measures adopted by GMO Internet Group amid this crisis underscore the organization’s resolve to safeguard its users and mitigate the impacts of cybercrime. As the investigation into the breach continues, the responsibility lies with the company and its customers to remain vigilant against further cyber threats.