
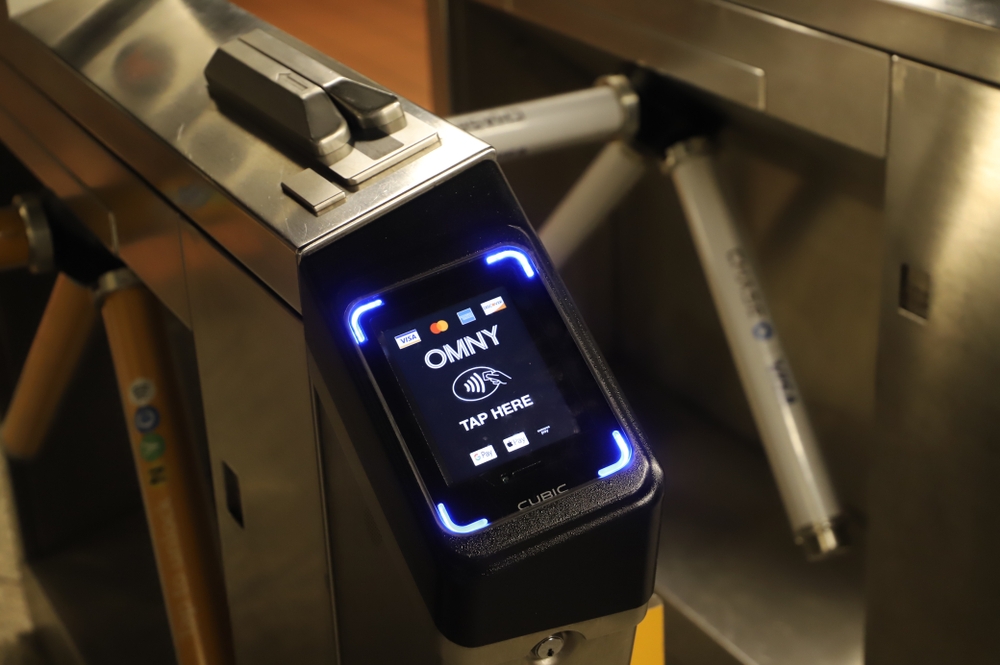


New York’s Metropolitan Transportation Authority (MTA) has temporarily disabled a feature associated with its contactless payment system due to a security vulnerability. The feature allowed individuals to access another person’s trip history on the city’s subway system by entering the card number used for tap-and-pay transactions into the MTA’s One Metro New York (OMNY) website. This raised concerns about privacy and the potential for stalking or tracking individuals.
A recent report by 404 Media highlighted this vulnerability, demonstrating how easy it was for someone to gain access to another person’s trip history without any additional verification. This raised concerns about the MTA’s use of credit card numbers as the primary identifier without requiring a PIN for authentication.
The availability of credit card numbers on underground markets further exacerbates the issue. According to a report by Comparitech, basic credit card information, including card number, CVV, expiration date, and cardholder name, can be purchased on the Dark Web for an average price of $17.36. This information can easily be used to track individuals and potentially invade their privacy.
OMNY’s trip history information only displays the point of entry into the subway system, which limits the extent of the information available. However, it still provides enough data for someone to stalk victims or narrow down their location. Privacy experts expressed concern over the lack of authentication and the potential risks associated with this feature.
In response to the report and concerns raised, the MTA has temporarily suspended the trip history feature on its OMNY website. MTA spokesman Eugene Resnick stated that the feature was meant to provide customers with access to their tap-and-go trip histories without creating an OMNY account. The MTA is now evaluating other ways to serve these customers while prioritizing customer privacy.
Despite this issue, the MTA continues to offer cash payment options and is open to input from safety experts for improving the contactless payment system’s security. The MTA introduced the tap-to-pay option for subway rides four years ago, allowing riders to use their contactless credit or debit cards or mobile wallets like Apple Pay or Google Pay.
To enhance security, the MTA tokenizes card numbers, obfuscating them as an additional security measure. This allows transactions to be processed and trip histories to be generated without the MTA ever knowing the actual credit card number.
The incident with the MTA highlights potential challenges organizations may face as they adopt tap-and-go payment models. While contactless payment technologies have gained popularity and are projected to reach a global value of $6.3 trillion by 2028, security concerns regarding payment card fraud and privacy breaches remain.
Currently, security concerns surrounding contactless payment technology are relatively muted, primarily focusing on the potential for payment card fraud. Criminals can take advantage of accidental loss or deliberate theft of debit or credit cards to make unauthorized purchases before a PIN is required.
As contactless payment systems continue to evolve and advance, it is crucial for organizations to prioritize security and privacy measures. Robust authentication methods and encryption techniques can help protect individuals’ sensitive information and prevent unauthorized access to personal data.
With the temporary suspension of the trip history feature, the MTA aims to address the vulnerability and find alternative ways to provide customers with access to their travel histories while ensuring their privacy and security. This incident serves as a reminder of the importance of ongoing evaluation and improvement to maintain the integrity and safety of contactless payment systems.