
OPTIMJACK: An Emerging Threat in Cybersecurity
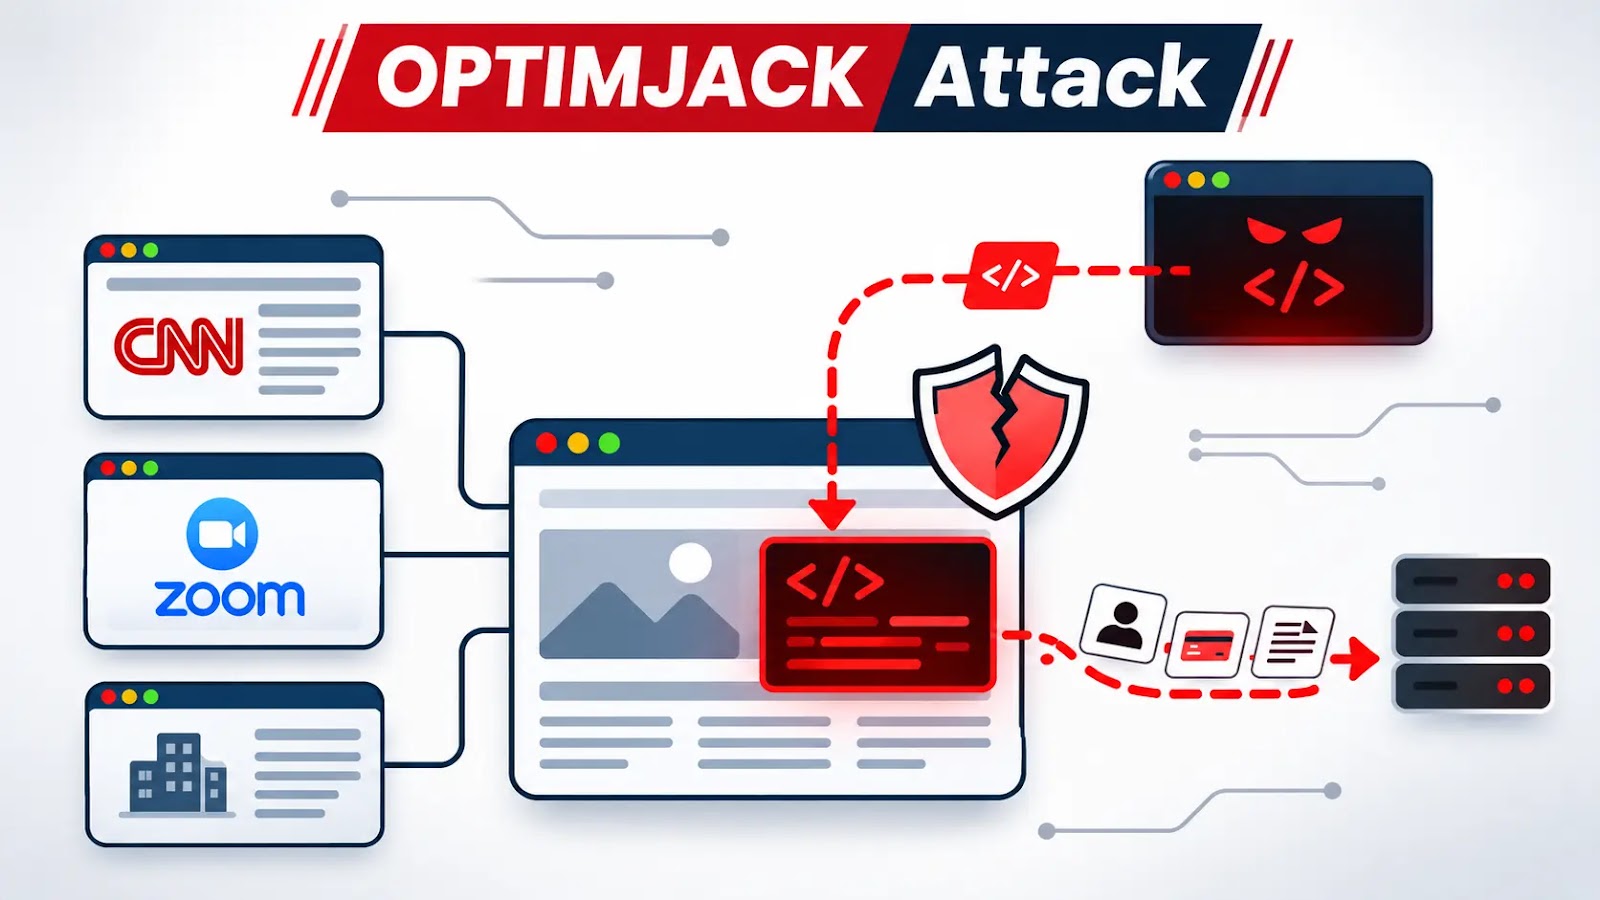
On November 16, cybersecurity researchers detected a malicious JavaScript delivery campaign dubbed OPTIMJACK, infiltrating prominent websites such as CNN, Zoom, and others through a third-party script layer. This alarming activity signals a grave concern for both users and website administrators, as it exploits trusted platforms to deliver potentially harmful code.
The observed malicious scripts are primarily designed to replace cryptocurrency wallet addresses, collect sensitive payment details, and selectively deliver additional content specifically to users browsing on iPhone and iPad devices. Although the success of financial theft and device exploitation remains unverified, the tactics employed suggest a well-orchestrated effort to exploit unsuspecting users.
The investigation of this campaign commenced when alerts from Cynet’s endpoint detection and response system flagged anomalous browser connections to the domain 1688360[.]cc. Following these alerts, CyOps analysts undertook a thorough examination of browsing activity, scrutinizing associated resources and tracing the malicious loader back to JavaScript served from cdn.optimizely[.]com. This identified the third-party script as the likely injection point; however, the precise method of insertion remains unclear.
Browser captures revealed that on sites like edition.cnn[.]com, a resource was appended to the page, directing users to 1688360[.]cc/track.js. Similar findings emerged from Zoom, where investigators detected the same insertion code embedded within an Optimizely-hosted script alongside standard Zoom resources. Remarkably, the same code was discovered while browsing Optimizely’s own website, raising questions about potential vulnerabilities in their systems.
In their investigation, the researchers expanded their focus to include other major organizations such as Salesforce, Fox News, and Fox Sports. However, the report lacked sufficient request-and-response captures to confirm these observations, leading to a differentiated status of evidence compared to the definitive cases involving CNN, Zoom, and Optimizely. It is crucial to note that the presence of scripts on these sites does not inherently imply that the internal systems of these organizations were compromised.
Potential entry routes for attackers may include compromised access to accounts, misconfigured tags, or vulnerable integrations. Yet, none of these pathways have been conclusively verified. Cynet emphasized that their findings should not be interpreted as definitive proof of a breach of Optimizely itself.
Further documentation from Cynet researchers indicated the presence of resources such as 1688360[.]cc/script.js and track.js, albeit the available evidence does not clarify whether these delivered identical payloads or represented various versions. Analysts describe the malicious functionality as being capable of substituting cryptocurrency addresses within page content or clipboard interactions, alongside logic aimed at collecting payment card details for transmission to an external server. Despite these capabilities, there is no evidence to support that a completed fraudulent transfer or successful data collection has occurred from the affected websites.
Other reported functionalities include the capability to gather accessible cookies and page data while utilizing html2canvas to render that content. However, the effectiveness of these operations is constrained by browser security protocols, evidenced by the lack of access to HttpOnly cookies, unrelated origins, other tabs, or unrestricted desktop screenshots.
Using device emulation akin to a Safari profile for iPhones, researchers investigated loading scripts from identified malicious infrastructure, including domains like 5vobauua3ojpklx[.]icu and eil786npto9u5bq[.]icu. The loader was reported to check various iOS versions and subsequently select what content to deliver through an iframe, including potential malicious payloads. Importantly, while this indicates conditional payload delivery, it does not confirm a successful breach of physical Apple devices.
As of now, no specific iOS version range, exploit common vulnerabilities and exposures (CVE), or attribution to threat actors has been established. Investigations into the root cause of the OPTIMJACK campaign and its overall impact are still ongoing.
In light of these findings, organizations are urged to review their third-party script configurations and tag setups vigilantly. They should also analyze historical data from DNS, proxy servers, and browser telemetry to identify the reported indicators. Security teams must manage to distinguish between blocked connections, executed JavaScript, and confirmed outbound data transfers. Preserving relevant data such as timestamps, headers, response bodies, and sample hashes will aid in reconstructing exposure scenarios linked to this threat.
Malicious domains identified in this campaign should be blocked through available DNS services, web gateways, and endpoint security controls, while testing for enforcement. Organizations must tread carefully, as broad restrictions affecting legitimate websites or shared delivery addresses could inadvertently cause collateral disruption.
Even after a subsequent 30-minute recheck, the scripts on the tested sites were not reproduced, leaving the question of universal removal unanswered. As a best practice, assessments should revolve around confirmed execution and potential exposure of visitor data rather than assuming every alert signifies an infection or confirmation of compromise within the underlying website or service.
In light of the escalating threats in today’s digital landscape, vigilance and preventative measures are paramount in shielding against sophisticated cyber-attacks like OPTIMJACK.