
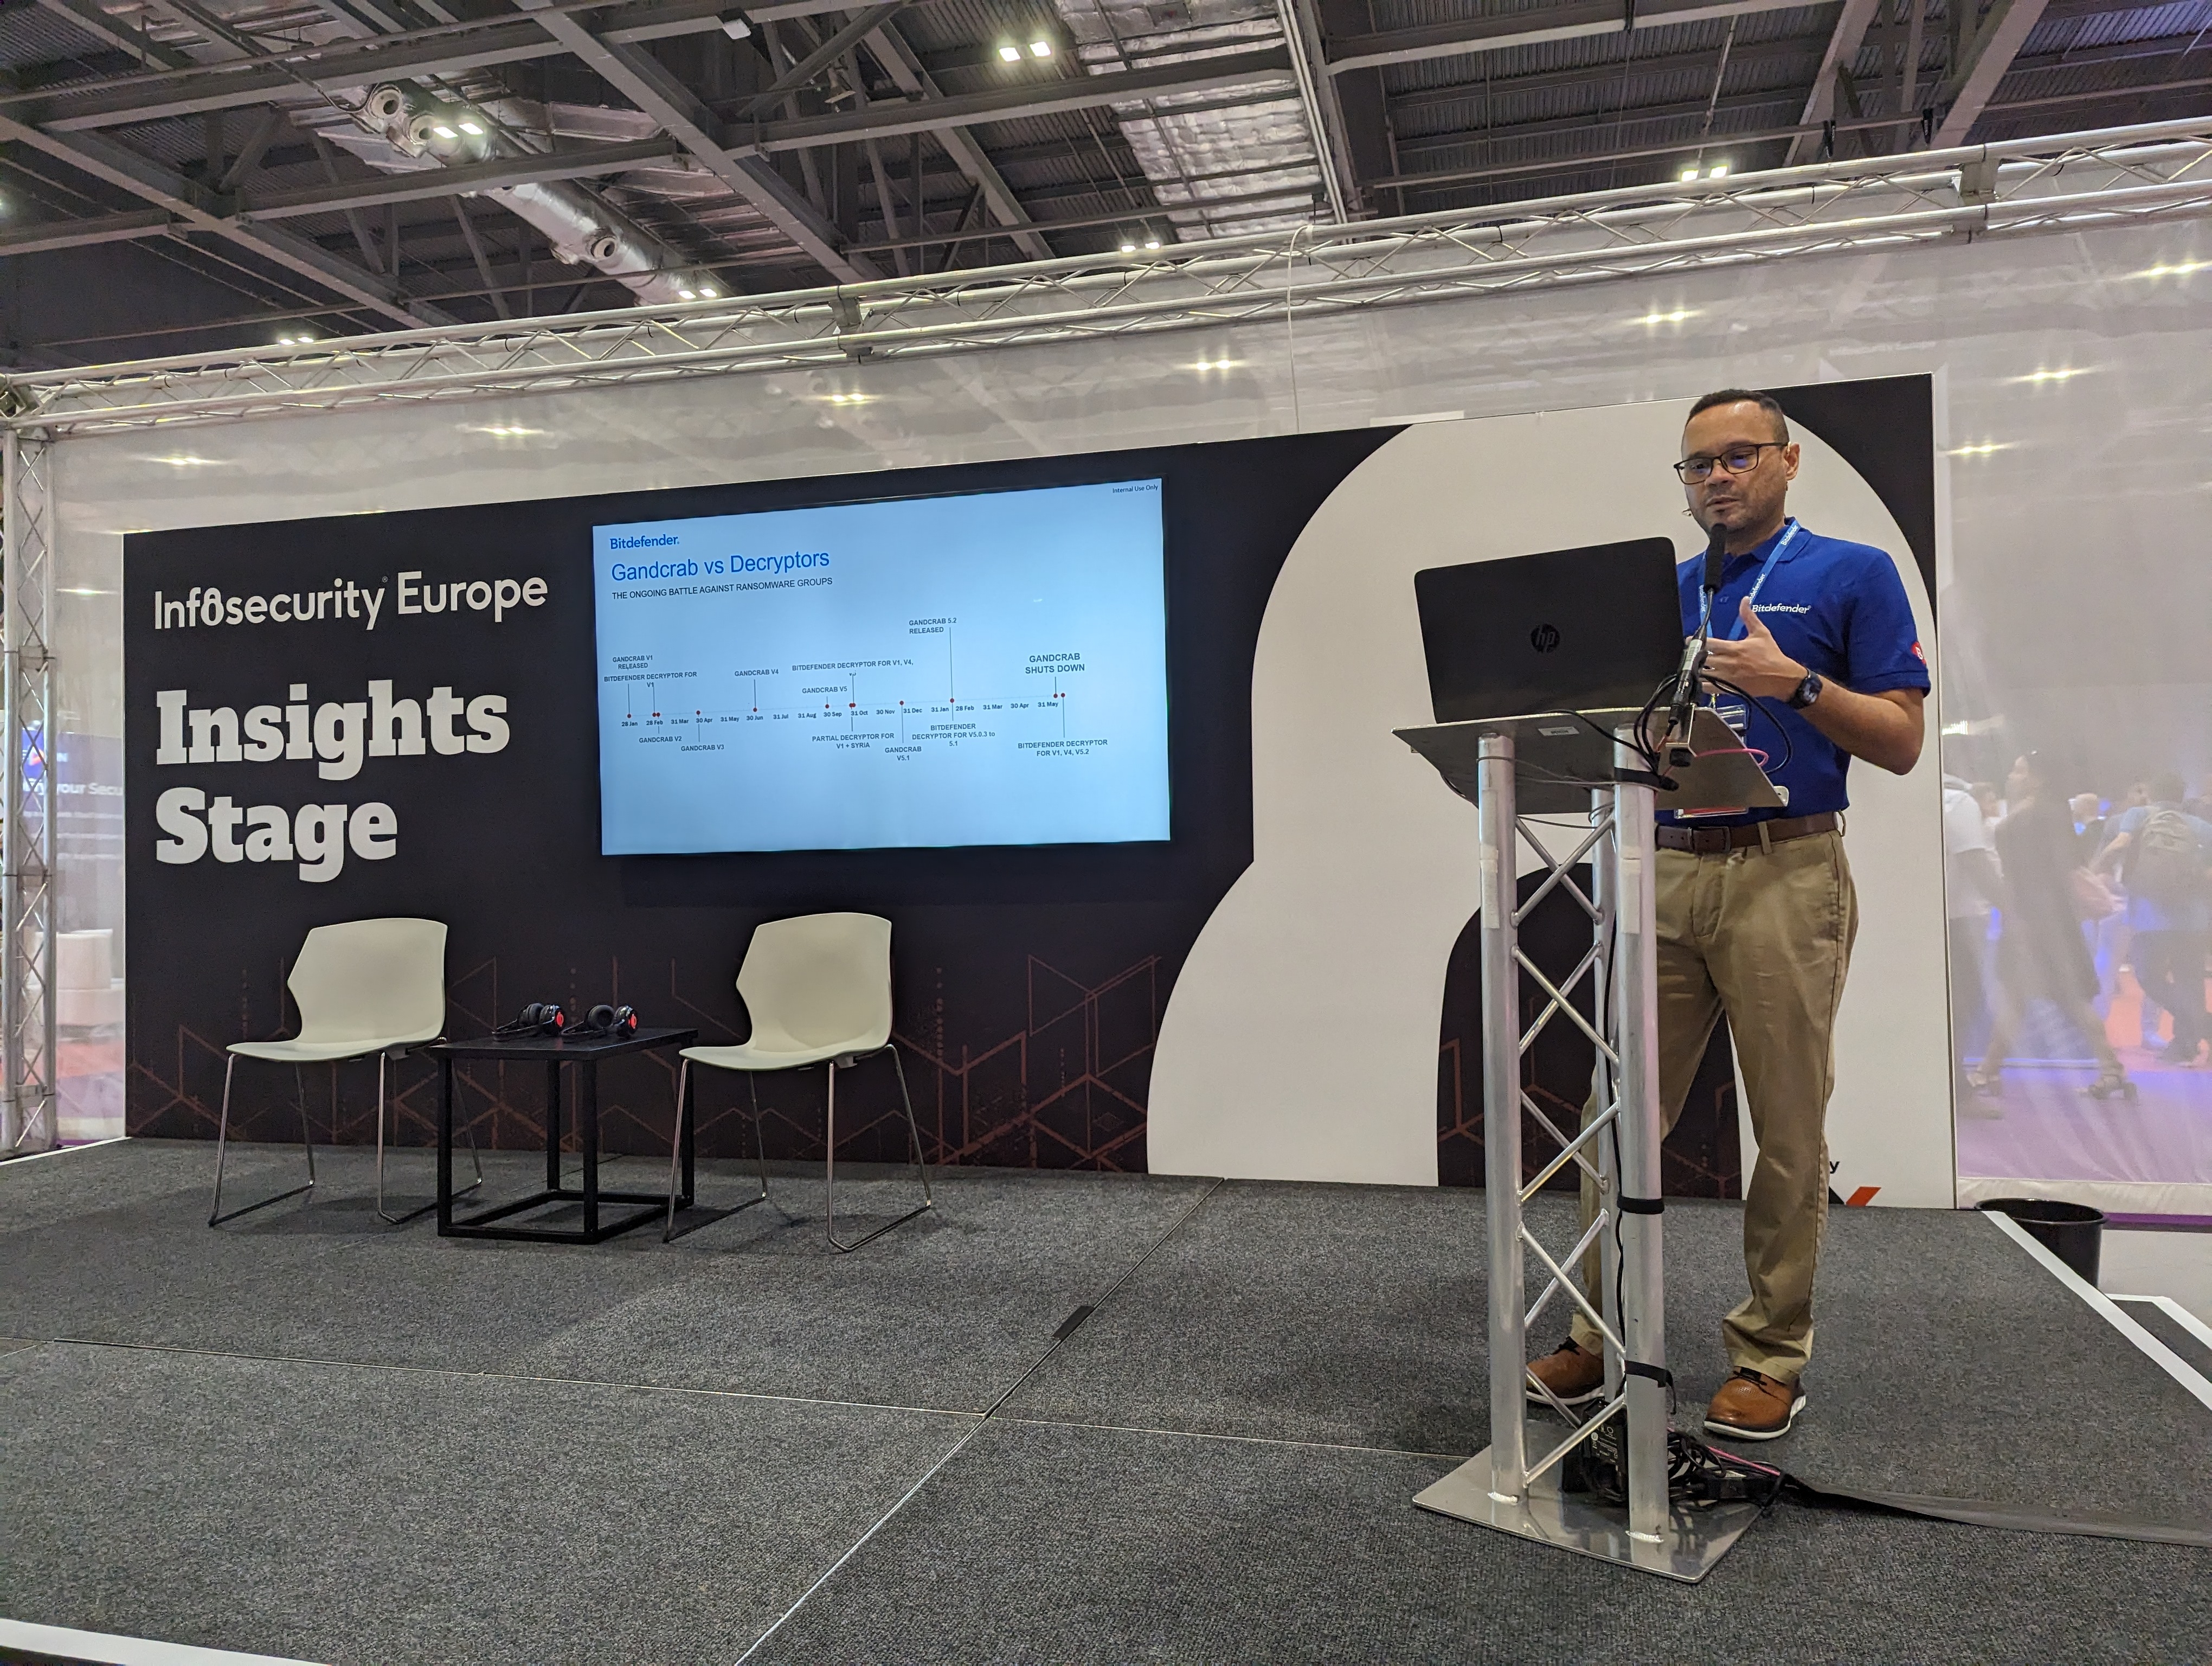


During his presentation at the Infosecurity Europe conference, Richard de la Torre, technical marketing manager at Bitdefender, shed light on some common myths and misconceptions surrounding ransomware. One of the prevailing misconceptions is that there is no way to combat ransomware effectively. However, de la Torre highlights that proactive organizations are increasingly utilizing decryptors and leveraging threat intelligence to prevent or disrupt ransomware attacks.
Despite the rise of ransomware-as-a-service and more sophisticated ransomware incidents, de la Torre asserts that the attack vectors for ransomware remain relatively basic. He explains that the threat process still begins with phishing attacks, emphasizing the need for organizations to combat email-based threats.
Furthermore, de la Torre emphasizes that ransomware has developed into a lucrative business. Driven by the ransomware-as-a-service business model, ransomware operators, sometimes even state-sponsored, buy and develop ransomware code, reselling it to affiliates who infiltrate networks. These organizations operate on a large scale, employing access brokers, data miners, and HR teams sourced from the dark and deep web.
Contrary to popular belief, a speedy response is not always necessary to prevent encryption and loss of business data. De la Torre reveals that most attackers now prioritize data exfiltration, using ransomware as a distraction while they steal sensitive information. In many cases, attackers maneuver within a network for prolonged periods, conducting reconnaissance to determine the presence of cyber insurance, identify key customers, and discover where the most valuable datasets are located.
Another myth that de la Torre dispels is the notion that attackers exclusively target large organizations. While larger organizations have dedicated resources and security operations center (SOC) teams, small organizations are often the primary targets. This is because smaller entities are seen as steppingstones to gaining unauthorized access to larger organizations through supply chain connections.
In terms of defense strategies, de la Torre recommends implementing a robust defense-in-depth posture. This includes deploying email security measures to prevent phishing attacks and adopting advanced detection and response solutions. Additionally, de la Torre emphasizes the importance of having tamper-proof systems in place and establishing effective data recovery mechanisms.
As ransomware continues to evolve, debunking these misconceptions is crucial for organizations to understand the true nature of the threat they face. By adopting proactive security measures and dispelling common myths, businesses can strengthen their defense against ransomware attacks and mitigate the potential impact on their operations.