
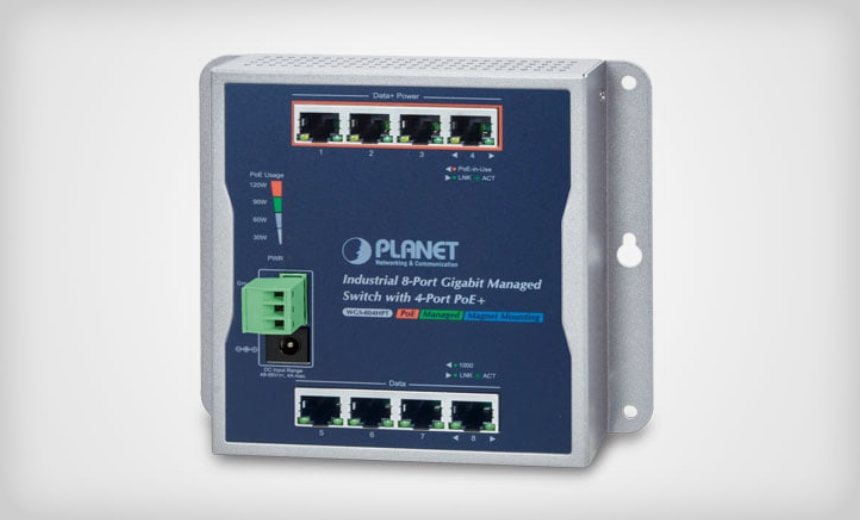


Researchers from Claroty’s Team82 recently discovered three critical vulnerabilities in industrial network switches, urging users to update their firmware to avoid potential exploitation by attackers. The vulnerabilities were found in WGS-804HPT switches manufactured by Planet Technology, which are commonly used in building and home automation networks to facilitate connectivity for IoT systems, IP surveillance cameras, and wireless LAN applications. These flaws could potentially allow attackers to gain remote control over automation systems, IoT devices, and surveillance networks.
Upon investigating the switches, Team82 identified multiple vulnerabilities in the web-based management interface, specifically in the dispatcher.cgi component. One of the vulnerabilities, tracked as CVE-2024-48871, is a stack-based buffer overflow with a CVSS score of 9.8, enabling remote code execution. The second flaw, CVE-2024-52320, also with a CVSS score of 9.8, involves an operating system command injection vulnerability that allows unauthenticated attackers to execute arbitrary commands. The third vulnerability, CVE-2024-52558, with a CVSS score of 5.3, is an integer underflow flaw that can crash the device using malformed HTTP requests, leading to service disruptions.
These findings highlight the risks associated with unpatched devices in critical automation networks, as attackers could exploit these vulnerabilities to gain unauthorized access, disrupt operations, or execute arbitrary commands on the compromised devices. It is crucial for users of these switches to apply the firmware update provided by Planet Technology to mitigate these security risks effectively.
The vulnerabilities in the dispatcher.cgi component were a result of improper input validation mechanisms, allowing attackers to bypass authentication checks and execute malicious commands with root privileges. Additionally, the lack of sanitization of user-supplied data made the switch susceptible to reflected cross-site scripting attacks, potentially compromising the sessions of authenticated administrators.
To address these vulnerabilities, Planet Technology released a patched firmware update in response to Claroty’s report. Team82 replicated the switch’s architecture to create a controlled environment for dissecting the firmware and identifying the critical flaws. The researchers emphasized the importance of regularly updating firmware and implementing security best practices to protect industrial network devices from potential cyber threats.
Overall, the discovery of these vulnerabilities underscores the need for robust cybersecurity measures in industrial networks to prevent unauthorized access and ensure the integrity and security of critical infrastructure. By staying vigilant and proactive in addressing security vulnerabilities, organizations can effectively safeguard their operational technology systems from potential cyber attacks.