
Exploit Targeting MDaemon Mail Server Software Poses Significant Risks
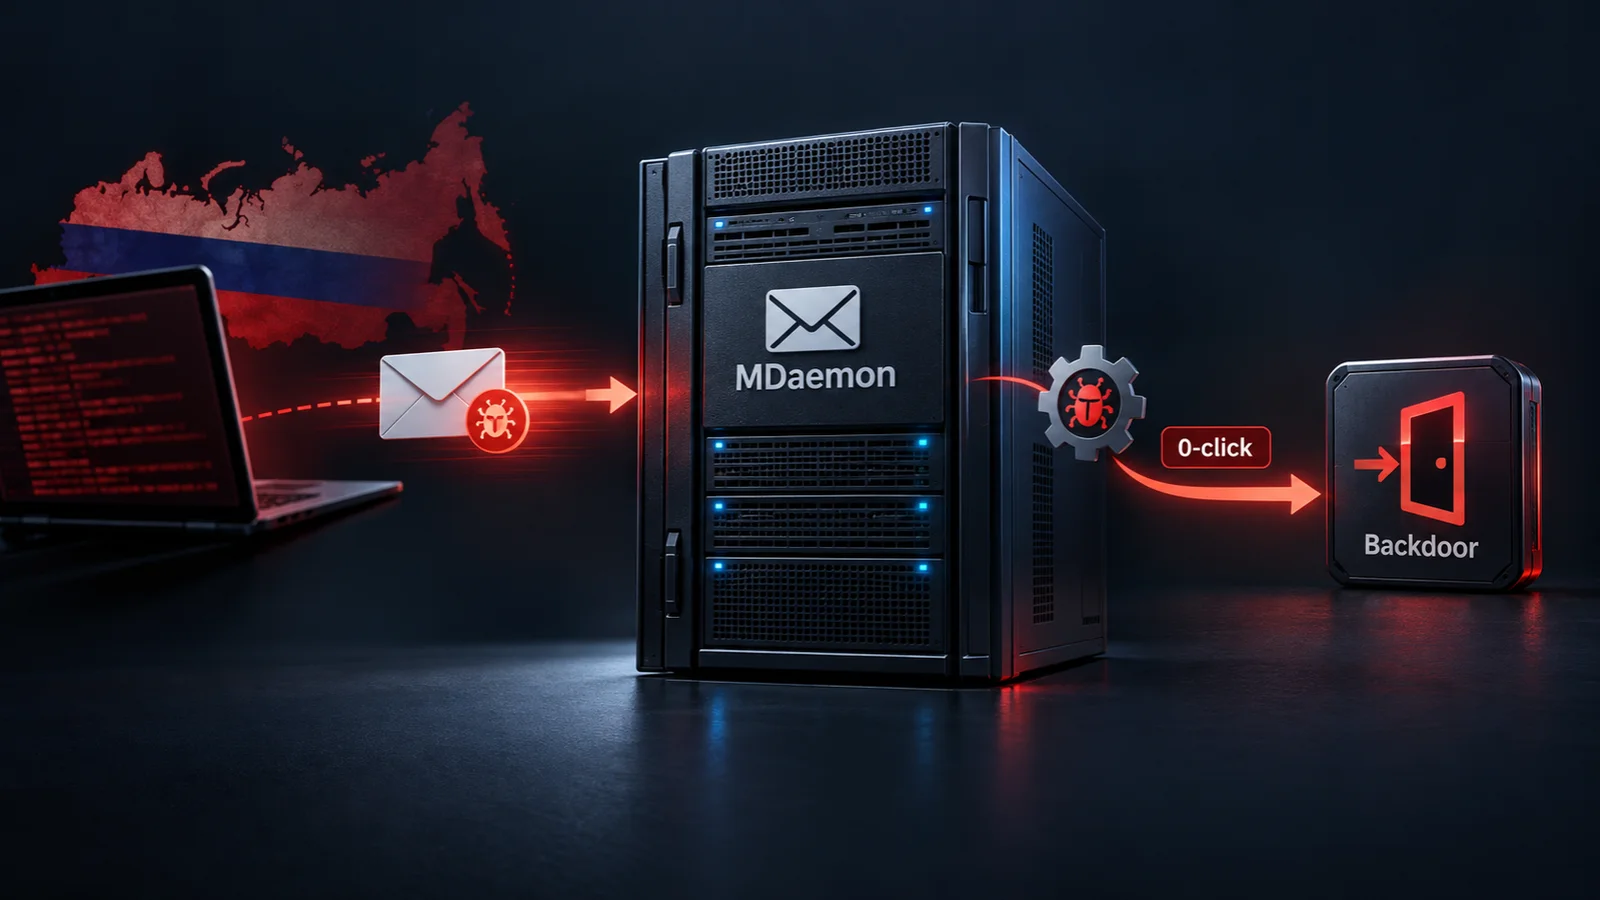
In a concerning development, threat actors aligned with Russian interests have been taking advantage of a vulnerability found in MDaemon mail server software. This exploit enables the attackers to execute unauthorized code on the server without requiring any interaction from the victims, such as opening an email or clicking on a link. This alarming capability heightens the risk for organizations across various sectors, especially those heavily reliant on email communications.
Active Campaigns in Ukraine
ESET’s APT Activity Report for the second and third quarters of 2026 documents an ongoing cyber campaign specifically targeting entities in Ukraine. Notably, ESET has refrained from linking this campaign to any recognized Russian-aligned hacking group, which underscores the complexity and evolving nature of the cyber threat landscape.
Understanding the MDaemon Mail Server Vulnerability
According to technical findings published by ESET, the MDaemon mail server software relies on ClamAV for scanning incoming email attachments. Unfortunately, older versions of ClamAV are still susceptible to the CVE-2025-8088 vulnerability, a flaw related to WinRAR path traversal, which ESET had identified last year. Although ClamAV issued a patch for the flaw on July 27, 2025, MDaemon continued to utilize an outdated version of the libclamunrar.dll library, leaving the server open to exploitation.
The mechanics of this attack are relatively straightforward yet insidious. Cybercriminals manipulate a malicious RAR archive that exploits the CVE-2025-8088 flaw. They then send this archive to any address associated with a vulnerable MDaemon server. Upon receiving the email, MDaemon utilizes ClamAV to scan the attachment, which inadvertently triggers the exploit. This process ultimately results in the malicious code being written to the mail server’s file system, thus compromising it.
The attackers employ a particularly stealthy method; there is no need for any form of deception, such as phishing or luring victims to click on malicious links. Instead, the exploit relies on the mail server’s built-in scanning mechanism to execute the attack autonomously.
A Broader Trend in Cyberattacks
This attack strategy is indicative of a broader pattern observed in the cyber activities of Russian-affiliated groups. They continue to exploit vulnerabilities in WinRAR, employing similar tactics against Ukrainian targets. The Computer Emergency Response Team of Ukraine (CERT-UA) has characterized two malware families involved in this campaign as HELLAGE and HELLTAG.
Mail servers, being repositories of sensitive communications, represent high-value targets for espionage-related initiatives. Previous Russian-aligned cyber campaigns have utilized vulnerabilities in webmail platforms to steal credentials and two-factor authentication secrets, further exemplifying the critical need for robust cybersecurity measures in this domain.
Mitigation Strategies and Recommendations
MDaemon addressed the vulnerability by releasing an updated version, 26.0.4, on August 25, 2026. However, organizations still operating on versions prior to this update that use the outdated ClamAV libraries remain susceptible to attack. For ClamAV, the corrected versions are 1.4.6 and 1.5.4.
To safeguard against these threats, defenders are urged to take immediate action. This includes upgrading MDaemon to version 26.0.4 or later and ensuring that the ClamAV libraries, especially libclamunrar.dll, are current. Additional recommendations for security teams consist of conducting thorough audits of the mail server file system to identify any unexpected DLL files residing outside of normal directories. They should also monitor for outbound connections to unknown command-and-control servers, scrutinize for Telegram bot API traffic emanating from the mail server, and review mailboxes for unauthorized access or bulk message exfiltration.
Organizations situated in Ukraine and throughout Europe are advised to treat any unpatched MDaemon servers as potentially compromised entities. The urgency for protective measures cannot be overstated, as the implications of such vulnerabilities can lead to significant breaches of sensitive information, furthering the threat landscape’s complexity and severity. Cyber defenders must remain vigilant and proactive to counter these rapidly evolving threats.