
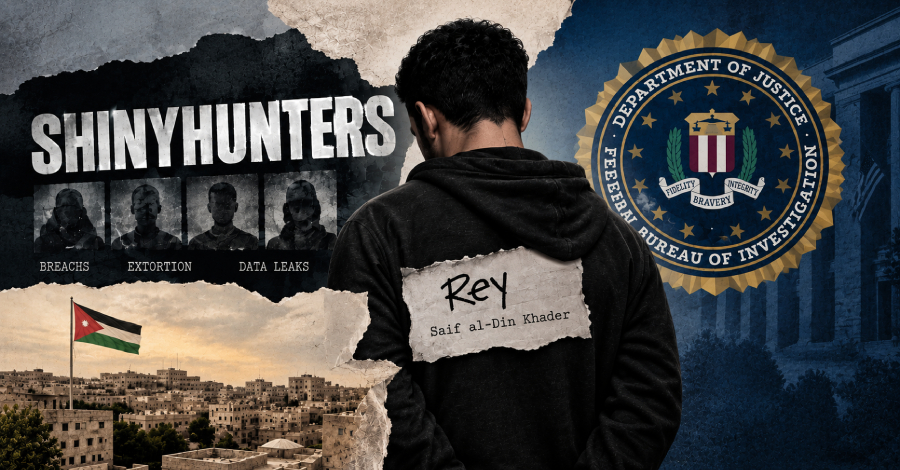
A significant development has emerged in the ongoing saga of the ShinyHunters digital extortion group, as authorities in Jordan reportedly apprehended a primary suspect known online as “Rey.” According to a recent report by Reuters, Rey, whose real name is Saif al-Din Khader, was taken into custody on September 29, 2026. This arrest marks a pivotal moment in the collaboration between law enforcement agencies, particularly the U.S. Federal Bureau of Investigation (FBI), and international authorities aimed at cracking down on cybercrime.
Sources close to the situation have indicated that Khader is cooperating with the FBI and other law enforcement agencies to help identify additional members of the ShinyHunters group. “His cooperation is critical to ongoing efforts to arrest these hackers,” one source stated, highlighting the strategic importance of Khader’s insights and collaborations for the ongoing investigations.
Rey is no stranger to the digital security community, having previously been identified as a pivotal figure in various cybercrime activities. In a November 2025 report by independent security journalist Brian Krebs, Khader was recognized as one of three administrators of the Scattered LAPSUS$ Hunters (SLH or SLSH), a collective viewed as an amalgamation of significant hacking groups including Scattered Spider and ShinyHunters. Krebs also noted that Khader previously managed the data leak platform for Hellcat, a ransomware group that emerged in late 2024, and had taken charge of the latest version of BreachForums during the same year. Notably, Khader had been cooperating with law enforcement since at least June 2025, demonstrating a long-standing connection to investigative efforts against cybercrime.
This arrest is a continuation of a series of legal actions against members of ShinyHunters, the most significant of which occurred just last week when a 24-year-old man from Amsterdam was apprehended for his involvement in the group’s illicit activities. Although his identity remains undisclosed, it has been suggested that he is Pepijn van der Stap, a reformed hacker currently working as an offensive security lead at the Dutch security firm Neo Security. Interestingly, ShinyHunters issued a statement denying any affiliation with van der Stap.
In a recent update, FBI Director Kash Patel emphasized the agency’s commitment to tackling cybercrime. “FBI teams are actively working with partners to obtain and execute more leads in the ongoing investigation based on this arrest,” Patel stated. He further reinforced the determination to identify and apprehend additional suspects, indicating, “FBI teams are working new leads RIGHT NOW. More arrests are on the table.”
The ShinyHunters group has garnered attention lately for its aggressive methods, including the hijacking of the darknet website operated by rival gang Cl0p. This operation exploited an unpatched vulnerability in Grav CMS and was part of a broader strategy that also included infiltrating the FBI’s application portal and stealing approximately three terabytes of sensitive information. In a statement, ShinyHunters maintained that their intent was not monetary gain concerning the FBI incident, but rather to challenge misleading allegations made by the agency regarding the group and its associations.
The FBI has made serious allegations against ShinyHunters, stating that the group, together with their accomplices, has breached over 140 organizations and extorted a minimum of $70 million in ransom payments. Brett Leatherman, assistant director of the FBI’s cyber division, emphasized the group’s focus on targeting third-party vendors within cloud platforms, allowing them to gain access to sensitive data that they subsequently threaten to publish unless their demands are met.
Leatherman also acknowledged the importance of collaboration within law enforcement efforts, calling on remaining group members to disclose information in light of current developments. “Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left. The longer you stay in this, the more we learn about you,” he cautioned.
In an insightful analysis of ShinyHunters’ evolution, cybersecurity firms like Sekoia and Beazley Security have traced the group’s origins back to two earlier hacking organizations, TheDarkOverlord and GnosticPlayers, which specialized in extortion and data leaks. The ShinyHunters brand made its public debut around April or May of 2020, and over the years has transformed from a small crew trading stolen databases into an expansive and intricate operation. Researchers have noted that while the group’s branding has endured, it has been characterized by a modular approach to tasks and responsibilities, which enhances resilience against law enforcement actions and fosters ongoing collaboration among various actors in the cybercrime world.
As the investigation unfolds and more information emerges, the implications of these arrests resonate beyond the immediate legal consequences. They highlight a broader narrative about the persistent and evolving threat posed by cybercriminals and the international efforts being made to combat this ongoing menace.