
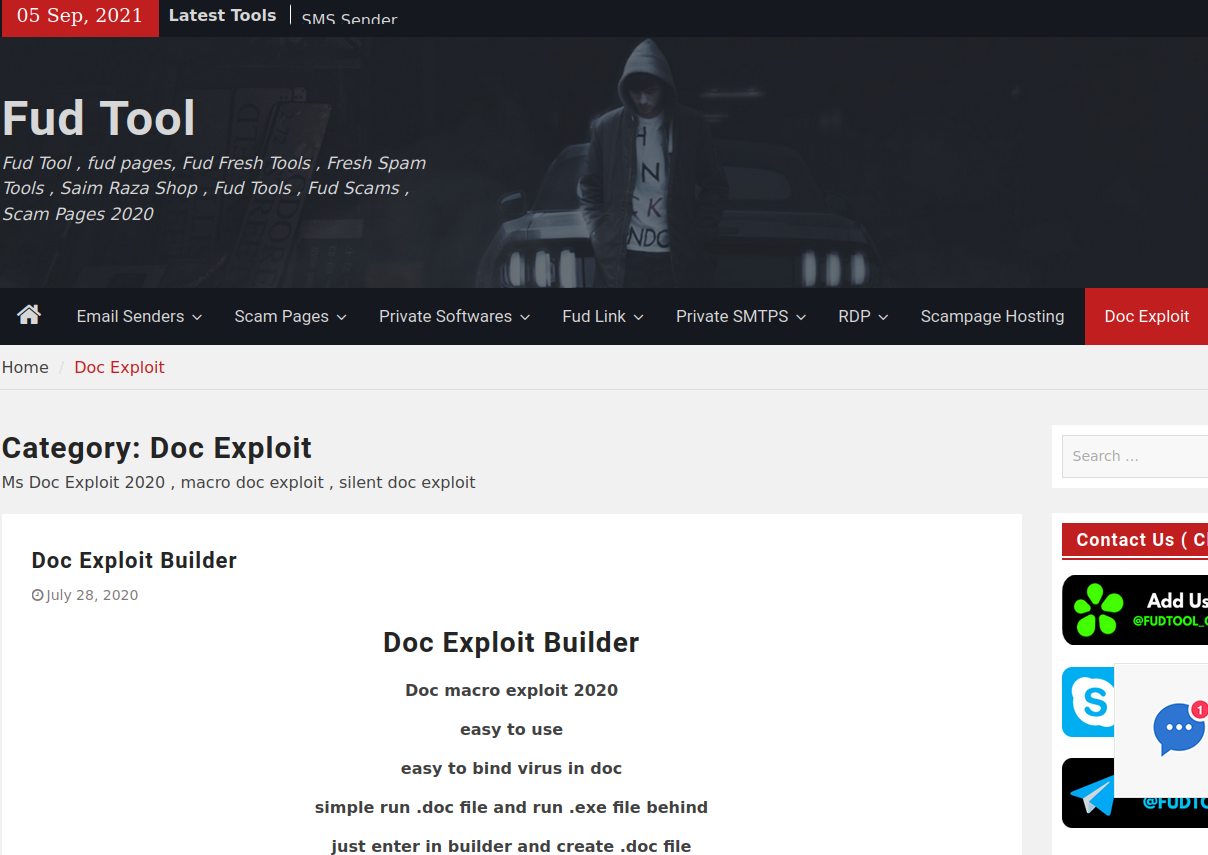


Dozens of servers and domains associated with a notorious spam and malware operation based in Pakistan were seized this week by the FBI and authorities in The Netherlands. The group, known collectively as “The Manipulaters,” has been under scrutiny since 2015 for their illegal activities. The main clients of this service are organized crime groups that utilize phishing and malware to deceive companies into making payments to a third party.
The cybercrime service, which includes brands such as Heartsender, Fudpage, and Fudtools, is specifically designed to evade detection by security tools like antivirus software and anti-spam appliances. The recent seizure by Dutch authorities involved 39 servers and domains located abroad, containing millions of records from victims worldwide, including about 100,000 records related to Dutch citizens.
The U.S. Department of Justice has identified the cybercrime group as “Saim Raza,” a pseudonym used by The Manipulaters to promote their illicit services on social media platforms. These services include phishing kits, scam pages, and email extractors used by organized crime groups to conduct business email compromise schemes. In such schemes, companies are tricked into making payments that are redirected to accounts controlled by the cybercriminals, leading to significant financial losses for the victims.
Heartsender, the primary product offered by The Manipulaters, is a spam delivery service that openly advertised phishing kits targeting users of popular internet companies like Microsoft 365, Yahoo, and iCloud. The disruption of this cybercrime group is aimed at halting the proliferation of tools used in fraudulent schemes and protecting potential victims.
The Manipulaters have been previously exposed for their activities, with investigations revealing their lack of concern for protecting their identity and their customers. DomainTools found that the group’s web-hosted version of Heartsender leaked sensitive user information, including credentials and email records. Additionally, evidence showed that the group’s computers were infected with password-stealing malware, leading to the theft and sale of numerous credentials online.
Authorities in The Netherlands are continuing their investigation into the owners and customers of the cybercrime service, with a focus on identifying buyers and potential Dutch nationals involved in the illegal activities. In a coordinated effort, law enforcement agencies in the U.S., Australia, France, Greece, Italy, Romania, and Spain also seized domains associated with longstanding cybercrime forums such as Cracked and Nulled, which collectively attracted millions of users.
The operation, known as “Operation Talent,” also targeted platforms like Sellix, an e-commerce platform used by cybercriminals to trade illicit goods and services. These efforts demonstrate a global commitment to combating cybercrime and protecting individuals and organizations from online threats. The investigation into The Manipulaters and other cybercrime operations is ongoing, with authorities working to dismantle these networks and hold those responsible accountable for their actions.