


Weekly Security Recap: Emerging Threats and Vulnerabilities in Focus
In the fast-paced realm of cybersecurity, one recent article highlights a concerning trend: attackers often employ new tactics that twist traditional methods into alarming features. A chilling example is the development of a tool designed specifically to siphon off data while simultaneously instilling fear in its victims. This escalation of threat sophistication has become a hallmark in this week’s security updates.
The landscape of cybersecurity is filled with unpredictable turns, as even minor permissions can snowball into major breaches. In some cases, what appears to be a trusted login can lead to a complete compromise of a system by masquerading as legitimate activity. Furthermore, older vulnerabilities are reportedly resurfacing, impacting new victims, while familiar tools are being repurposed in unsettling ways. Some flaws are so rudimentary that it’s astonishing how they could have overlooked for so long.
Active Ransomware Exploitation
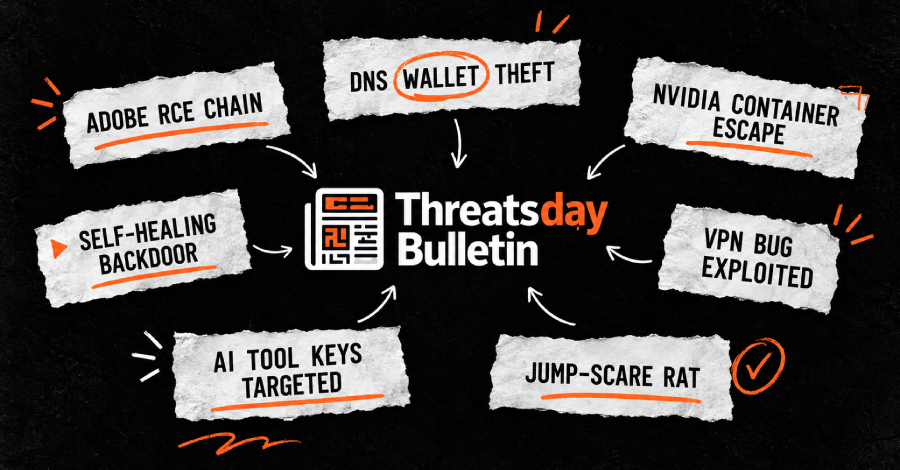
One of the most critical threats currently is the active exploitation of a vulnerability in PAN-OS called CVE-2026-0257. Ransomware groups like Qilin and Settra are taking advantage of this authentication bypass flaw within PAN-OS GlobalProtect and Prisma Access. Originally disclosed in May 2026, it has been on their radar ever since. Since the access is gained through an organization’s VPN, attackers can operate undetected, mimicking legitimate remote work activities. Security experts from ReliaQuest are urging organizations to swiftly patch their systems and investigate unexpected connections, especially those linked to unusual hostnames like "kali."
Escalation of Hybrid Warfare in Europe
Another significant report indicates a worrying trend in hybrid warfare tactics employed by Russia. Following its full-scale invasion of Ukraine, the country has seemingly intensified its use of asymmetrical warfare throughout Europe. According to analysis from Recorded Future, these tactics do not involve direct military confrontations but instead consist of a mix of psychological, cyber, and physical maneuvers aimed at testing enemy defenses, crippling critical infrastructure, and creating an environment of fear among governments and civilian populations.
Emerging Threats in Cryptocurrency and Remote Access
Notably, there has been a surge in sophisticated attacks targeting cryptocurrency wallets. An analysis by Infoblox reveals a toolkit, named Noir, designed to drain cryptocurrency wallets through clever utilization of DNS TXT records, making it challenging to trace its origins. This malware operates without the need for a seed phrase or private key, allowing it to obtain spending permissions covertly.
Additionally, a concerning Rust-based remote access trojan, known as CikaBika Bot, is being distributed through document-themed lure files. The malware utilizes a series of methods for exploitation, including PowerShell UAC bypass, and relies on platforms like Discord for command and control, data exfiltration, and remote executions.
Intimidation Tactics in Malware
Among the more disturbing developments is the marketing of KGB RAT, a remote access trojan found on underground forums. This malware not only offers credential theft and ransomware capabilities but also includes features designed to intimidate its victims, such as screamer functions and forced blue screens of death. The developers have equipped it with psychological harassment tools, making it a multifaceted weapon in the hands of cybercriminals.
Enhancements in Android and Browser Security
On the defensive side, Google is making strides to bolster Android’s security against mobile scams. The tech giant is rolling out advanced protection mechanisms across Google Messages, including scam detection powered by Private AI Compute and real-time verification for bank calls in collaboration with various financial institutions.
Simultaneously, Mozilla has introduced Firefox Enterprise, targeting organizations needing strict security measures and governance. This new iteration is ostensibly designed to enhance IT control over data and infrastructure.
Drawbacks of Oversight
Despite the advancements in cybersecurity, a persistent theme remains clear: attackers frequently exploit simple oversights. Whether it’s a stolen login, a minor misconfiguration, or a forgotten vulnerability, these gaps can open the door to severe compromises.
As organizations analyze their security protocols, there’s an urgent need not only to check for what is visibly broken but also to scrutinize who has gained access, what data they have interacted with, and whether they possess lingering access rights.
Conclusion
The complexities of today’s cybersecurity environment signal that vigilance must remain a constant. Understanding the layers of threats and being proactive in addressing vulnerabilities is essential in safeguarding sensitive data. With each edition of weekly security reports, the lessons learned underline the importance of not overlooking the simple components that can lead to monumental issues. As we look to the future, the hope remains that the upcoming week will yield fewer unexpected security threats.
Stay informed and prepared.