
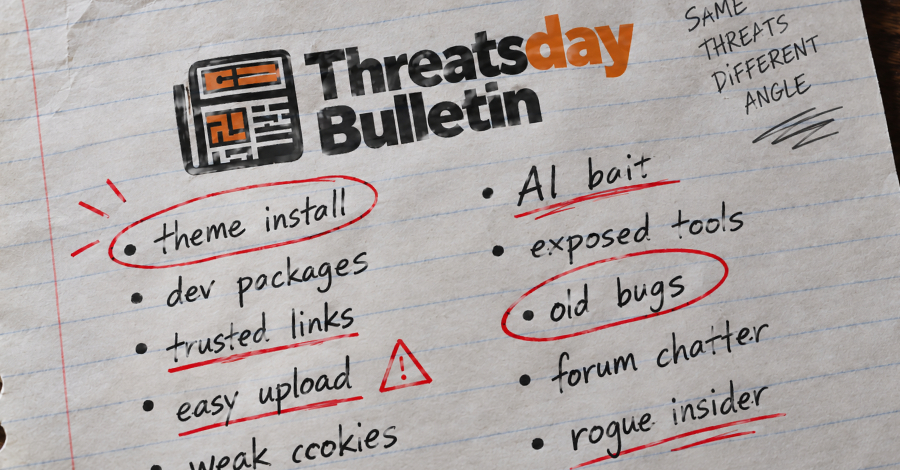


The realm of cybersecurity is continually evolving, revealing a striking juxtaposition between the blunders of malicious actors and the vulnerabilities of the systems they exploit. This week, several hacking incidents shed light on the inadequacies present in both criminal and victim organizations, emphasizing a shared inability to maintain security protocols effectively.
One notable incident involved a ransomware affiliate identified as Azazel, who operated within the Gentlemen ransomware group. Azazel demonstrated a significant breach of trust within his criminal organization by pocketing profits gained from extortion attempts against around two dozen victims across six countries. Instead of sharing the proceeds with his associates, he opted to publish the stolen data on a private leak site he had created, cleverly branded as “Leakned.” This audacious move not only undermined the group’s cohesion but also highlighted that internal trust issues plague even the most unscrupulous of enterprises.
In another instance, an attacker left a server exposed, containing tools and traces of a previously executed intrusion. This negligence serves as a stark reminder that cybersecurity is fraught with challenges on both sides of the fence—criminals often overlook basic security measures in their eagerness to exploit vulnerabilities, while the systems targeted exhibit similar failings.
The remainder of the week brought further unsettling revelations. Malicious code was found embedded in developer packages and extensions, masquerading as innocuous tools. Popular online services inadvertently facilitated phishing emails, lending them an air of legitimacy that can deceive unsuspecting users. A basic flaw in file upload protocols granted attackers unencumbered access into systems, and vulnerability in session cookie design made impersonation alarmingly easy. Notably, artificial intelligence (AI) assistants are now also being manipulated, with phishing messages designed to influence their behavior effectively.
A deeper analysis of these incidents reveals a fascinating gap between the effort required to execute a successful attack and the outcomes achieved. While some attacks are meticulously planned, involving multiple stages and intricate strategies, others capitalize on mere design flaws or oversights that often go unchecked. This disparity indicates that both sophisticated and rudimentary approaches yield successful exploits when systems remain inadequately secured.
The threats observed this week are diverse and troubling, reflecting the fusing of creativity and negligence that characterizes contemporary cybercrime.
One alarming discovery involved malicious themes available in the Visual Studio Marketplace, disguised as harmless color themes but linked to previously removed extensions harboring nefarious intentions. Research conducted by Socket unveiled the connection between these themes and a dangerous malware strain known as GlassWorm, capable of executing highly sophisticated cyberattacks using a complex infrastructure.
Additionally, a campaign utilizing WhatsApp to distribute a financial-document lure was unveiled. The file, titled “Statement.exe,” delivered a previously monitored remote access trojan (RAT) dubbed VulcanRAT207, demonstrating how attackers are adapting popular platforms to spread malware effectively.
In parallel developments, an alarming report emerged from Forescout, indicating that a significant proportion of medical devices are largely unprepared for future quantum-enabled cyber threats. A review of over 2.5 million devices revealed that a mere fraction possess the capability to support post-quantum cryptography, leaving sensitive healthcare data acutely vulnerable to potential future attacks.
Even more concerning is the revelation of a troubling authentication bypass in a yard management system attributed to two critical weaknesses in its session-cookie design. This oversight could allow malicious actors to forge session tokens for arbitrary users, exposing employees to significant risks, including privileged account impersonation.
Further insights came from the ongoing international effort to combat large-scale cyber scam operations. FBI Director Kash Patel announced that “Operation Blackout” has led to the seizure of $17 billion and the apprehension of hundreds involved in scams targeting vulnerable populations, particularly the elderly. Patel highlighted the fluidity of these criminal networks, which constantly adapt to evade law enforcement, making the need for ongoing vigilance crucial.
As the week progressed, cybersecurity professionals observed a pattern where even attackers exhibit a surprising lack of caution, leaving their operational tools open to discovery while simultaneously targeting systems with insecure designs. This ironic oversight not only emphasizes the carelessness of many involved but also reflects a broader, systemic issue in cybersecurity, where foundational weaknesses allow breaches to proliferate.
Overall, the reports from this week serve as a reminder that complacency exists in the digital landscape, and the need for improved security measures, thorough system audits, and a proactive approach toward cybersecurity must remain at the forefront of organizational priorities. While the actors may be careless, the consequences of their actions are anything but trivial, making it imperative to address the myriad challenges highlighted in these incidents. A heightened awareness of design flaws, coupled with an understanding of emerging threats, is essential to safeguarding vital infrastructure and sensitive data in an increasingly interconnected world.