
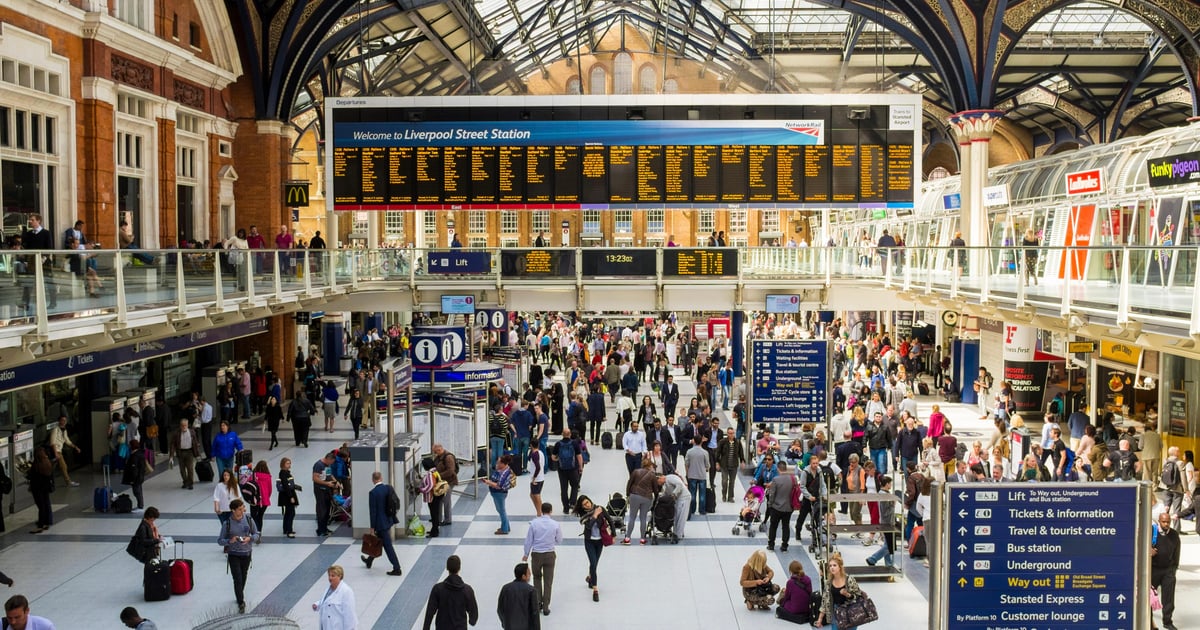


A cybersecurity incident that resulted in the display of Islamophobic messages to users through compromised Wi-Fi landing pages is currently under investigation. The incident occurred at 20 stations managed by Network Rail, a non-departmental public body, with 10 of the affected stations located in London and the others spread across key commuter stations in Reading, Leeds, Glasgow Central, and beyond.
The British Transport Police (BTP) were alerted to the cyberattack at approximately 1703 on September 25th and have since been involved in the case alongside Network Rail. Telent, the communications company responsible for operating Network Rail’s Wi-Fi services, has acknowledged the incident and is actively participating in the investigation to determine the root cause.
Experts in the field of cybersecurity have noted the increasing trend of nation states and criminal entities targeting third-party suppliers to orchestrate large-scale disruptions across multiple industries simultaneously. Dan Schiappa, the chief product and services officer at Arctic Wolf, emphasized the importance of ensuring that all companies, regardless of their critical infrastructure status, collaborate with suppliers who have robust cybersecurity measures in place to prevent vulnerabilities in their defenses.
As the investigation unfolds, Network Rail has taken the precautionary measure of suspending Wi-Fi services to prevent any further dissemination of offensive messages. While it remains unclear who may be responsible for the cyberattack, the focus is on identifying the source and implementing necessary measures to enhance the security of Wi-Fi services across the affected stations.
It is critical for organizations to prioritize cybersecurity and establish secure protocols when partnering with external vendors to safeguard against potential threats and vulnerabilities. The incident serves as a reminder of the ongoing risks posed by cyber threats and highlights the need for proactive measures to mitigate future incidents of a similar nature.
With the cooperation of relevant authorities and cybersecurity experts, Network Rail aims to swiftly address the security breach and restore normal operations to ensure the safety and well-being of passengers and staff. The incident underscores the importance of diligence in cybersecurity practices and serves as a wake-up call for organizations to enhance their readiness in the face of evolving cyber threats.